PSA cryptography module: Mbed TLS structured type implementations. More...
#include "mbedtls/private_access.h"#include "psa/build_info.h"#include "psa/crypto_driver_contexts_primitives.h"#include "psa/crypto_driver_contexts_composites.h"#include "psa/crypto_driver_contexts_key_derivation.h"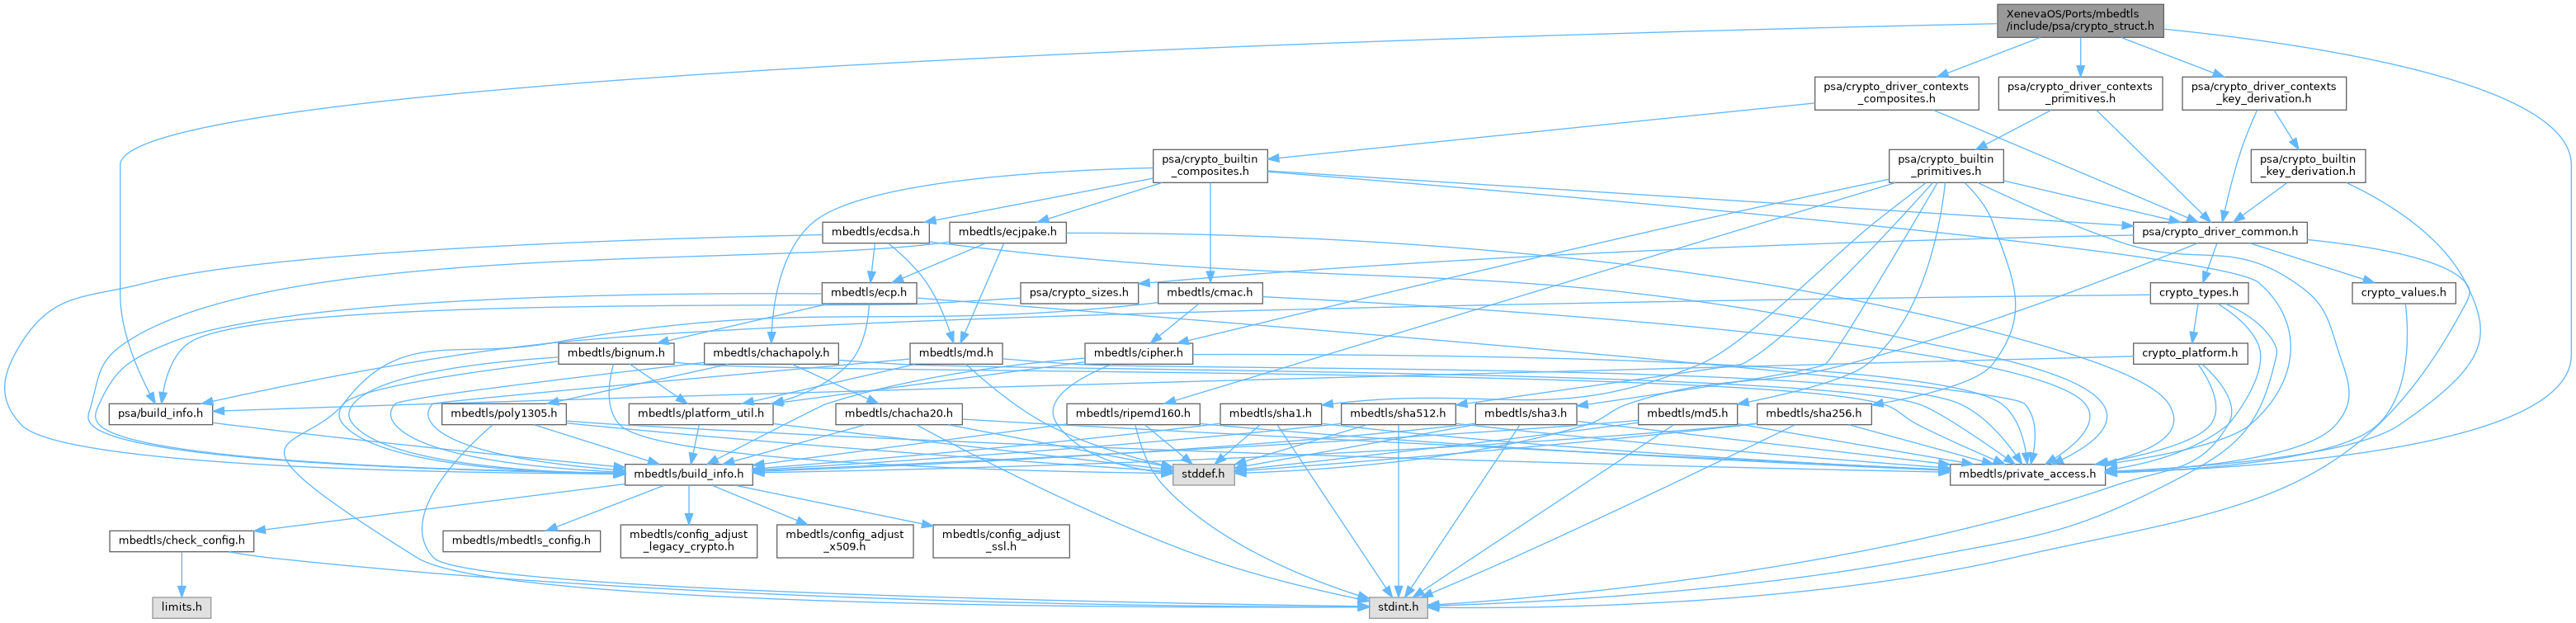
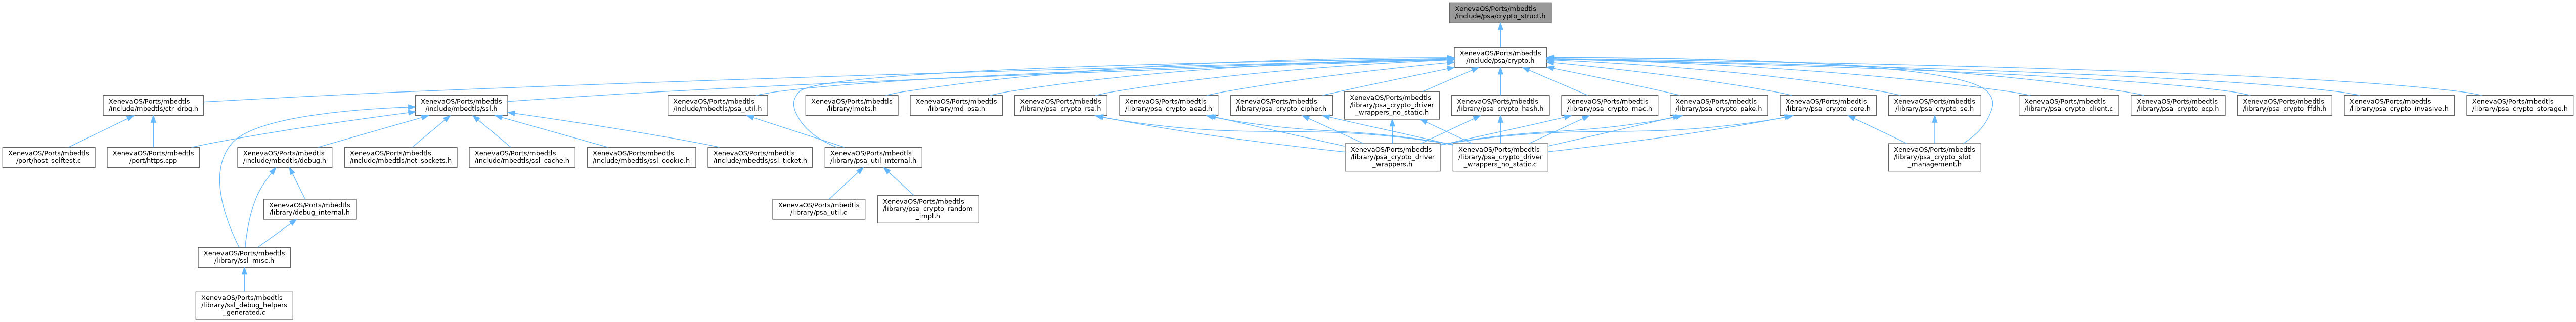
Go to the source code of this file.
Classes | |
| struct | psa_hash_operation_s |
| struct | psa_cipher_operation_s |
| struct | psa_mac_operation_s |
| struct | psa_aead_operation_s |
| struct | psa_key_derivation_s |
| struct | psa_custom_key_parameters_s |
| struct | psa_key_production_parameters_s |
| struct | psa_key_policy_s |
| struct | psa_key_attributes_s |
| struct | psa_sign_hash_interruptible_operation_s |
| The context for PSA interruptible hash signing. More... | |
| struct | psa_verify_hash_interruptible_operation_s |
| The context for PSA interruptible hash verification. More... | |
Macros | |
| #define | PSA_HASH_OPERATION_INIT { 0, { 0 } } |
| #define | PSA_CIPHER_OPERATION_INIT { 0, 0, 0, 0, { 0 } } |
| #define | PSA_MAC_OPERATION_INIT { 0, 0, 0, { 0 } } |
| #define | PSA_AEAD_OPERATION_INIT { 0, 0, 0, 0, 0, 0, 0, 0, 0, 0, { 0 } } |
| #define | PSA_KEY_DERIVATION_OPERATION_INIT { 0, 0, 0, { 0 } } |
| #define | PSA_CUSTOM_KEY_PARAMETERS_INIT { 0 } |
| #define | PSA_KEY_PRODUCTION_PARAMETERS_INIT { 0 } |
| #define | PSA_KEY_POLICY_INIT { 0, 0, 0 } |
| #define | PSA_KEY_BITS_TOO_LARGE ((psa_key_bits_t) -1) |
| #define | PSA_MAX_KEY_BITS 0xfff8 |
| #define | PSA_KEY_ATTRIBUTES_MAYBE_SLOT_NUMBER |
| #define | PSA_KEY_ATTRIBUTES_INIT |
| #define | PSA_SIGN_HASH_INTERRUPTIBLE_OPERATION_INIT { 0, { 0 }, 0, 0 } |
| #define | PSA_VERIFY_HASH_INTERRUPTIBLE_OPERATION_INIT { 0, { 0 }, 0, 0 } |
Typedefs | |
| typedef struct psa_key_policy_s | psa_key_policy_t |
| typedef uint16_t | psa_key_bits_t |
Detailed Description
PSA cryptography module: Mbed TLS structured type implementations.
- Note
- This file may not be included directly. Applications must include psa/crypto.h.
This file contains the definitions of some data structures with implementation-specific definitions.
In implementations with isolation between the application and the cryptography module, it is expected that the front-end and the back-end would have different versions of this file.
Design notes about multipart operation structures
For multipart operations without driver delegation support, each multipart operation structure contains a psa_algorithm_t alg field which indicates which specific algorithm the structure is for. When the structure is not in use, alg is 0. Most of the structure consists of a union which is discriminated by alg.
For multipart operations with driver delegation support, each multipart operation structure contains an unsigned int id field indicating which driver got assigned to do the operation. When the structure is not in use, 'id' is 0. The structure contains also a driver context which is the union of the contexts of all drivers able to handle the type of multipart operation.
Note that when alg or id is 0, the content of other fields is undefined. In particular, it is not guaranteed that a freshly-initialized structure is all-zero: we initialize structures to something like {0, 0}, which is only guaranteed to initializes the first member of the union; GCC and Clang initialize the whole structure to 0 (at the time of writing), but MSVC and CompCert don't.
In Mbed TLS, multipart operation structures live independently from the key. This allows Mbed TLS to free the key objects when destroying a key slot. If a multipart operation needs to remember the key after the setup function returns, the operation structure needs to contain a copy of the key.
Macro Definition Documentation
◆ PSA_CUSTOM_KEY_PARAMETERS_INIT
| #define PSA_CUSTOM_KEY_PARAMETERS_INIT { 0 } |
The default production parameters for key generation or key derivation.
Calling psa_generate_key_custom() or psa_key_derivation_output_key_custom() with custom=PSA_CUSTOM_KEY_PARAMETERS_INIT and custom_data_length=0 is equivalent to calling psa_generate_key() or psa_key_derivation_output_key() respectively.
◆ PSA_KEY_ATTRIBUTES_MAYBE_SLOT_NUMBER
| #define PSA_KEY_ATTRIBUTES_MAYBE_SLOT_NUMBER |
◆ PSA_KEY_BITS_TOO_LARGE
| #define PSA_KEY_BITS_TOO_LARGE ((psa_key_bits_t) -1) |
◆ PSA_KEY_POLICY_INIT
| #define PSA_KEY_POLICY_INIT { 0, 0, 0 } |
◆ PSA_KEY_PRODUCTION_PARAMETERS_INIT
| #define PSA_KEY_PRODUCTION_PARAMETERS_INIT { 0 } |
The default production parameters for key generation or key derivation.
Calling psa_generate_key_ext() or psa_key_derivation_output_key_ext() with params=PSA_KEY_PRODUCTION_PARAMETERS_INIT and params_data_length == 0 is equivalent to calling psa_generate_key() or psa_key_derivation_output_key() respectively.
◆ PSA_MAX_KEY_BITS
| #define PSA_MAX_KEY_BITS 0xfff8 |
◆ PSA_SIGN_HASH_INTERRUPTIBLE_OPERATION_INIT
| #define PSA_SIGN_HASH_INTERRUPTIBLE_OPERATION_INIT { 0, { 0 }, 0, 0 } |
◆ PSA_VERIFY_HASH_INTERRUPTIBLE_OPERATION_INIT
| #define PSA_VERIFY_HASH_INTERRUPTIBLE_OPERATION_INIT { 0, { 0 }, 0, 0 } |
Typedef Documentation
◆ psa_key_bits_t
| typedef uint16_t psa_key_bits_t |
◆ psa_key_policy_t
| typedef struct psa_key_policy_s psa_key_policy_t |
