Include dependency graph for psa_crypto_ecp.h:
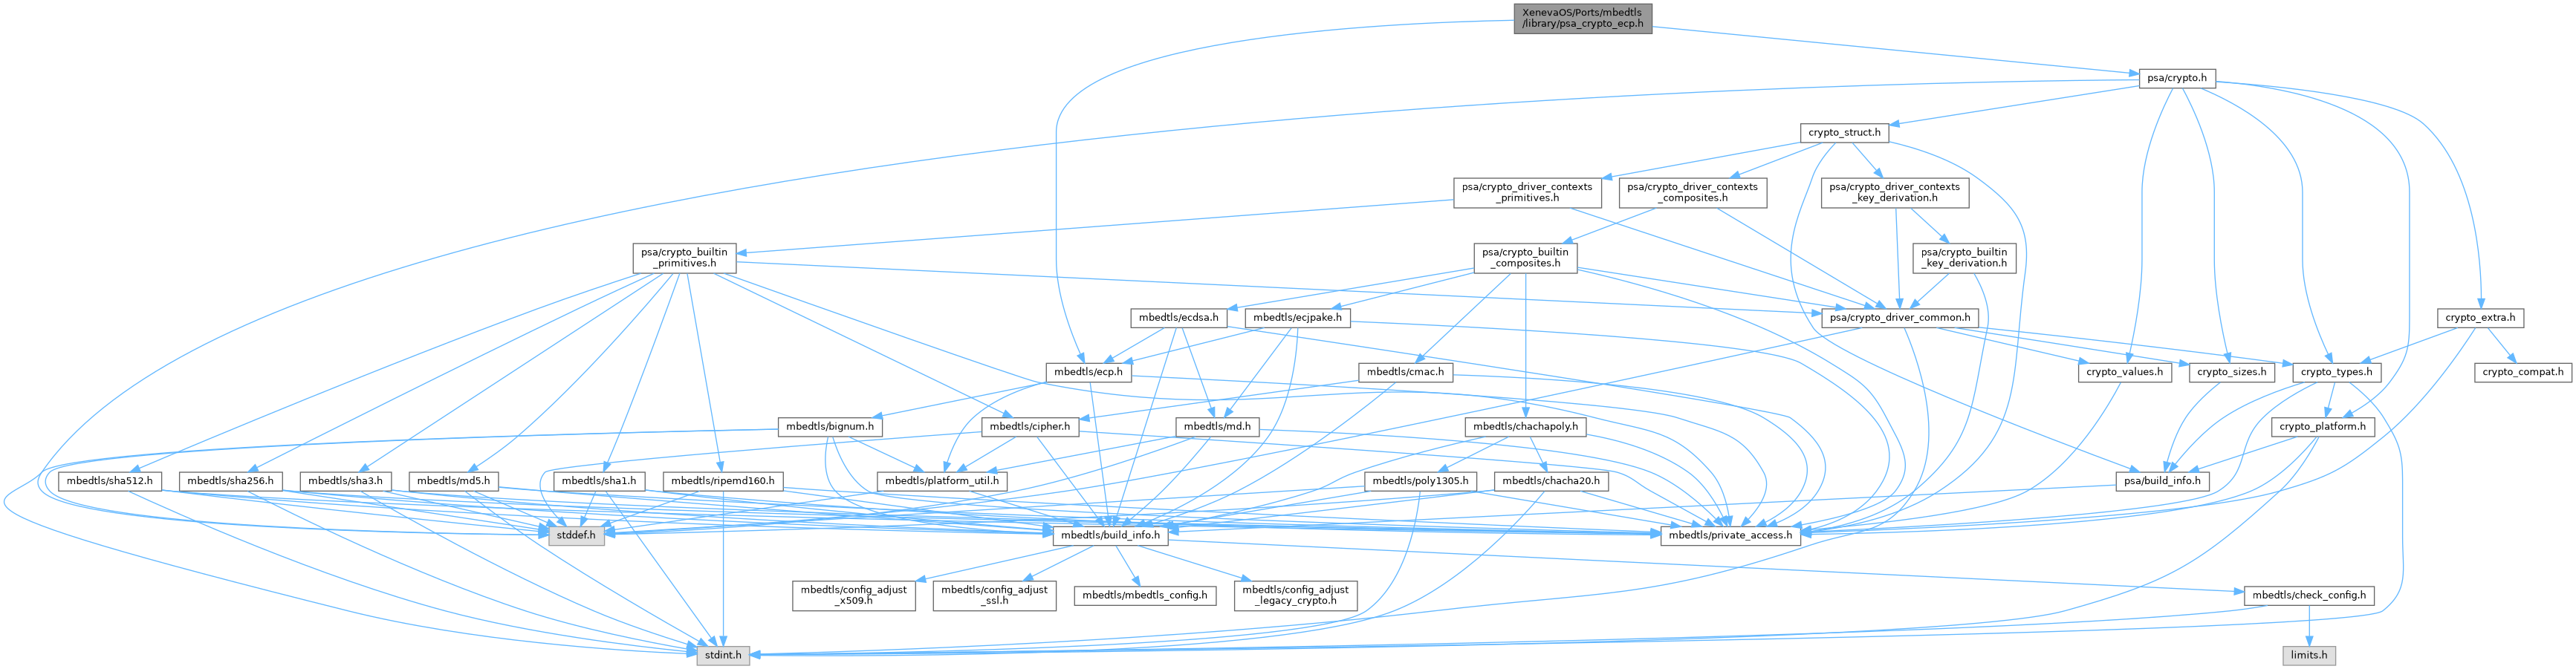
Go to the source code of this file.
Functions | |
| psa_status_t | mbedtls_psa_ecp_load_representation (psa_key_type_t type, size_t curve_bits, const uint8_t *data, size_t data_length, mbedtls_ecp_keypair **p_ecp) |
| psa_status_t | mbedtls_psa_ecp_load_public_part (mbedtls_ecp_keypair *ecp) |
| psa_status_t | mbedtls_psa_ecp_import_key (const psa_key_attributes_t *attributes, const uint8_t *data, size_t data_length, uint8_t *key_buffer, size_t key_buffer_size, size_t *key_buffer_length, size_t *bits) |
| psa_status_t | mbedtls_psa_ecp_export_key (psa_key_type_t type, mbedtls_ecp_keypair *ecp, uint8_t *data, size_t data_size, size_t *data_length) |
| psa_status_t | mbedtls_psa_ecp_export_public_key (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, uint8_t *data, size_t data_size, size_t *data_length) |
| psa_status_t | mbedtls_psa_ecp_generate_key (const psa_key_attributes_t *attributes, uint8_t *key_buffer, size_t key_buffer_size, size_t *key_buffer_length) |
| Generate an ECP key. | |
| psa_status_t | mbedtls_psa_ecdsa_sign_hash (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *hash, size_t hash_length, uint8_t *signature, size_t signature_size, size_t *signature_length) |
| psa_status_t | mbedtls_psa_ecdsa_verify_hash (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *hash, size_t hash_length, const uint8_t *signature, size_t signature_length) |
| Verify an ECDSA hash or short message signature. | |
| psa_status_t | mbedtls_psa_key_agreement_ecdh (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *peer_key, size_t peer_key_length, uint8_t *shared_secret, size_t shared_secret_size, size_t *shared_secret_length) |
Function Documentation
◆ mbedtls_psa_ecdsa_sign_hash()
| psa_status_t mbedtls_psa_ecdsa_sign_hash | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | hash, | ||
| size_t | hash_length, | ||
| uint8_t * | signature, | ||
| size_t | signature_size, | ||
| size_t * | signature_length | ||
| ) |
Sign an already-calculated hash with ECDSA.
- Note
- The signature of this function is that of a PSA driver sign_hash entry point. This function behaves as a sign_hash entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes of the ECC key to use for the operation. [in] key_buffer The buffer containing the ECC key context. format. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[in] alg Randomized or deterministic ECDSA algorithm. [in] hash The hash or message to sign. [in] hash_length Size of the hashbuffer in bytes.[out] signature Buffer where the signature is to be written. [in] signature_size Size of the signaturebuffer in bytes.[out] signature_length On success, the number of bytes that make up the returned signature value.
- Return values
-
PSA_SUCCESS \emptydescription PSA_ERROR_BUFFER_TOO_SMALL The size of the signaturebuffer is too small. You can determine a sufficient buffer size by calling PSA_SIGN_OUTPUT_SIZE(PSA_KEY_TYPE_ECC_KEY_PAIR,key_bits,alg) wherekey_bitsis the bit-size of the ECC key.PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_INSUFFICIENT_ENTROPY \emptydescription
◆ mbedtls_psa_ecdsa_verify_hash()
| psa_status_t mbedtls_psa_ecdsa_verify_hash | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | hash, | ||
| size_t | hash_length, | ||
| const uint8_t * | signature, | ||
| size_t | signature_length | ||
| ) |
Verify an ECDSA hash or short message signature.
- Note
- The signature of this function is that of a PSA driver verify_hash entry point. This function behaves as a verify_hash entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes of the ECC key to use for the operation. [in] key_buffer The buffer containing the ECC key context. format. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[in] alg Randomized or deterministic ECDSA algorithm. [in] hash The hash or message whose signature is to be verified. [in] hash_length Size of the hashbuffer in bytes.[in] signature Buffer containing the signature to verify. [in] signature_length Size of the signaturebuffer in bytes.
- Return values
-
PSA_SUCCESS The signature is valid. PSA_ERROR_INVALID_SIGNATURE The calculation was performed successfully, but the passed signature is not a valid signature. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription
◆ mbedtls_psa_ecp_export_key()
| psa_status_t mbedtls_psa_ecp_export_key | ( | psa_key_type_t | type, |
| mbedtls_ecp_keypair * | ecp, | ||
| uint8_t * | data, | ||
| size_t | data_size, | ||
| size_t * | data_length | ||
| ) |
Export an ECP key to export representation
- Parameters
-
[in] type The type of key (public/private) to export [in] ecp The internal ECP representation from which to export [out] data The buffer to export to [in] data_size The length of the buffer to export to [out] data_length The amount of bytes written to data
◆ mbedtls_psa_ecp_export_public_key()
| psa_status_t mbedtls_psa_ecp_export_public_key | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| uint8_t * | data, | ||
| size_t | data_size, | ||
| size_t * | data_length | ||
| ) |
Export an ECP public key or the public part of an ECP key pair in binary format.
- Note
- The signature of this function is that of a PSA driver export_public_key entry point. This function behaves as an export_public_key entry point as defined in the PSA driver interface specification.
- Parameters
-
[in] attributes The attributes for the key to export. [in] key_buffer Material or context of the key to export. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[out] data Buffer where the key data is to be written. [in] data_size Size of the databuffer in bytes.[out] data_length On success, the number of bytes written in data
- Return values
-
PSA_SUCCESS The ECP public key was exported successfully. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_COMMUNICATION_FAILURE \emptydescription PSA_ERROR_HARDWARE_FAILURE \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_STORAGE_FAILURE \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription
◆ mbedtls_psa_ecp_generate_key()
| psa_status_t mbedtls_psa_ecp_generate_key | ( | const psa_key_attributes_t * | attributes, |
| uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| size_t * | key_buffer_length | ||
| ) |
Generate an ECP key.
- Note
- The signature of the function is that of a PSA driver generate_key entry point.
- Parameters
-
[in] attributes The attributes for the ECP key to generate. [out] key_buffer Buffer where the key data is to be written. [in] key_buffer_size Size of key_bufferin bytes.[out] key_buffer_length On success, the number of bytes written in key_buffer.
- Return values
-
PSA_SUCCESS The key was successfully generated. PSA_ERROR_NOT_SUPPORTED Key length or type not supported. PSA_ERROR_BUFFER_TOO_SMALL The size of key_bufferis too small.
◆ mbedtls_psa_ecp_import_key()
| psa_status_t mbedtls_psa_ecp_import_key | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | data, | ||
| size_t | data_length, | ||
| uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| size_t * | key_buffer_length, | ||
| size_t * | bits | ||
| ) |
Import an ECP key in binary format.
- Note
- The signature of this function is that of a PSA driver import_key entry point. This function behaves as an import_key entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes for the key to import. [in] data The buffer containing the key data in import format. [in] data_length Size of the databuffer in bytes.[out] key_buffer The buffer containing the key data in output format. [in] key_buffer_size Size of the key_bufferbuffer in bytes. This size is greater or equal todata_length.[out] key_buffer_length The length of the data written in key_bufferin bytes.[out] bits The key size in number of bits.
- Return values
-
PSA_SUCCESS The ECP key was imported successfully. PSA_ERROR_INVALID_ARGUMENT The key data is not correctly formatted. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription
◆ mbedtls_psa_ecp_load_public_part()
| psa_status_t mbedtls_psa_ecp_load_public_part | ( | mbedtls_ecp_keypair * | ecp | ) |
Load the public part of an internal ECP, if required.
- Parameters
-
ecp The ECP context to load the public part for.
- Returns
- PSA_SUCCESS on success, otherwise an MPI error.
◆ mbedtls_psa_ecp_load_representation()
| psa_status_t mbedtls_psa_ecp_load_representation | ( | psa_key_type_t | type, |
| size_t | curve_bits, | ||
| const uint8_t * | data, | ||
| size_t | data_length, | ||
| mbedtls_ecp_keypair ** | p_ecp | ||
| ) |
Load the contents of a key buffer into an internal ECP representation
- Parameters
-
[in] type The type of key contained in data.[in] curve_bits The nominal bit-size of the curve. It must be consistent with the representation passed in data. This can be 0, in which case the bit-size is inferred fromdata_length(which is possible for all key types and representation formats formats that are currently supported or will be in the foreseeable future).[in] data The buffer from which to load the representation. [in] data_length The size in bytes of data.[out] p_ecp Returns a pointer to an ECP context on success. The caller is responsible for freeing both the contents of the context and the context itself when done.
◆ mbedtls_psa_key_agreement_ecdh()
| psa_status_t mbedtls_psa_key_agreement_ecdh | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | peer_key, | ||
| size_t | peer_key_length, | ||
| uint8_t * | shared_secret, | ||
| size_t | shared_secret_size, | ||
| size_t * | shared_secret_length | ||
| ) |
Perform a key agreement and return the raw ECDH shared secret.
- Note
- The signature of this function is that of a PSA driver key_agreement entry point. This function behaves as a key_agreement entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes of the key to use for the operation. [in] key_buffer The buffer containing the private key context. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[in] alg A key agreement algorithm that is compatible with the type of the key. [in] peer_key The buffer containing the key context of the peer's public key. [in] peer_key_length Size of the peer_keybuffer in bytes.[out] shared_secret The buffer to which the shared secret is to be written. [in] shared_secret_size Size of the shared_secretbuffer in bytes.[out] shared_secret_length On success, the number of bytes that make up the returned shared secret.
- Return values
-
PSA_SUCCESS Success. Shared secret successfully calculated. PSA_ERROR_INVALID_HANDLE \emptydescription PSA_ERROR_NOT_PERMITTED \emptydescription PSA_ERROR_INVALID_ARGUMENT algis not a key agreement algorithm, orprivate_keyis not compatible withalg, orpeer_keyis not valid foralgor not compatible withprivate_key.PSA_ERROR_BUFFER_TOO_SMALL shared_secret_sizeis too smallPSA_ERROR_NOT_SUPPORTED algis not a supported key agreement algorithm.PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription
