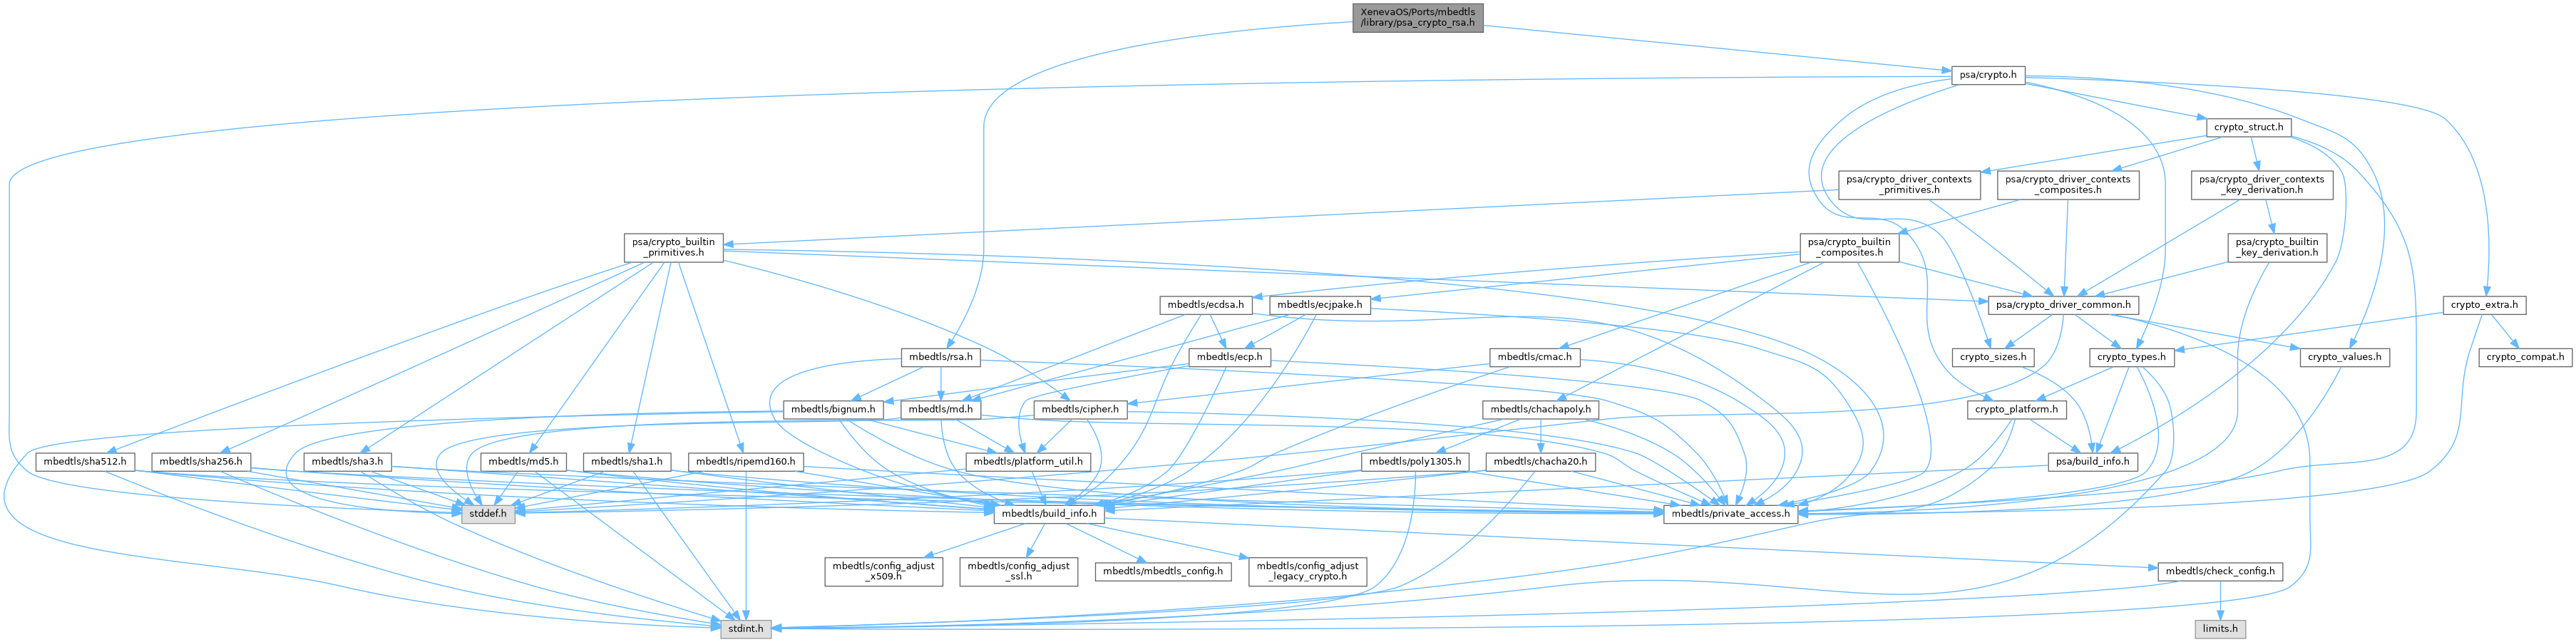
Include dependency graph for psa_crypto_rsa.h:
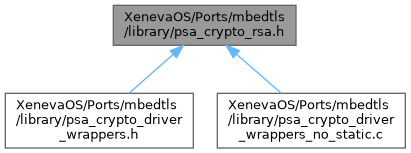
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Functions | |
| psa_status_t | mbedtls_psa_rsa_load_representation (psa_key_type_t type, const uint8_t *data, size_t data_length, mbedtls_rsa_context **p_rsa) |
| psa_status_t | mbedtls_psa_rsa_import_key (const psa_key_attributes_t *attributes, const uint8_t *data, size_t data_length, uint8_t *key_buffer, size_t key_buffer_size, size_t *key_buffer_length, size_t *bits) |
| psa_status_t | mbedtls_psa_rsa_export_key (psa_key_type_t type, mbedtls_rsa_context *rsa, uint8_t *data, size_t data_size, size_t *data_length) |
| psa_status_t | mbedtls_psa_rsa_export_public_key (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, uint8_t *data, size_t data_size, size_t *data_length) |
| psa_status_t | mbedtls_psa_rsa_generate_key (const psa_key_attributes_t *attributes, const uint8_t *custom_data, size_t custom_data_length, uint8_t *key_buffer, size_t key_buffer_size, size_t *key_buffer_length) |
| Generate an RSA key. | |
| psa_status_t | mbedtls_psa_rsa_sign_hash (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *hash, size_t hash_length, uint8_t *signature, size_t signature_size, size_t *signature_length) |
| psa_status_t | mbedtls_psa_rsa_verify_hash (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *hash, size_t hash_length, const uint8_t *signature, size_t signature_length) |
| Verify the signature a hash or short message using a public RSA key. | |
| psa_status_t | mbedtls_psa_asymmetric_encrypt (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *input, size_t input_length, const uint8_t *salt, size_t salt_length, uint8_t *output, size_t output_size, size_t *output_length) |
| Encrypt a short message with a public key. | |
| psa_status_t | mbedtls_psa_asymmetric_decrypt (const psa_key_attributes_t *attributes, const uint8_t *key_buffer, size_t key_buffer_size, psa_algorithm_t alg, const uint8_t *input, size_t input_length, const uint8_t *salt, size_t salt_length, uint8_t *output, size_t output_size, size_t *output_length) |
| Decrypt a short message with a private key. | |
Function Documentation
◆ mbedtls_psa_asymmetric_decrypt()
| psa_status_t mbedtls_psa_asymmetric_decrypt | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | input, | ||
| size_t | input_length, | ||
| const uint8_t * | salt, | ||
| size_t | salt_length, | ||
| uint8_t * | output, | ||
| size_t | output_size, | ||
| size_t * | output_length | ||
| ) |
Decrypt a short message with a private key.
- Parameters
-
attributes The attributes for the key to import. key_buffer Buffer where the key data is to be written. key_buffer_size Size of the key_bufferbuffer in bytes.[in] input The message to decrypt. input_length Size of the inputbuffer in bytes.[in] salt A salt or label, if supported by the encryption algorithm. If the algorithm does not support a salt, pass NULL. If the algorithm supports an optional salt and you do not want to pass a salt, passNULL.
- For PSA_ALG_RSA_PKCS1V15_CRYPT, no salt is supported.
- Parameters
-
salt_length Size of the saltbuffer in bytes. IfsaltisNULL, pass 0.[out] output Buffer where the decrypted message is to be written. output_size Size of the outputbuffer in bytes.[out] output_length On success, the number of bytes that make up the returned output.
- Return values
-
PSA_SUCCESS \emptydescription PSA_ERROR_BUFFER_TOO_SMALL The size of the outputbuffer is too small. You can determine a sufficient buffer size by calling PSA_ASYMMETRIC_DECRYPT_OUTPUT_SIZE(key_type,key_bits,alg) wherekey_typeandkey_bitsare the type and bit-size respectively ofkey.PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_COMMUNICATION_FAILURE \emptydescription PSA_ERROR_HARDWARE_FAILURE \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_INSUFFICIENT_ENTROPY \emptydescription PSA_ERROR_INVALID_PADDING \emptydescription PSA_ERROR_BAD_STATE The library has not been previously initialized by psa_crypto_init(). It is implementation-dependent whether a failure to initialize results in this error code.
◆ mbedtls_psa_asymmetric_encrypt()
| psa_status_t mbedtls_psa_asymmetric_encrypt | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | input, | ||
| size_t | input_length, | ||
| const uint8_t * | salt, | ||
| size_t | salt_length, | ||
| uint8_t * | output, | ||
| size_t | output_size, | ||
| size_t * | output_length | ||
| ) |
Encrypt a short message with a public key.
- Parameters
-
attributes The attributes for the key to import. key_buffer Buffer where the key data is to be written. key_buffer_size Size of the key_bufferbuffer in bytes.input_length Size of the inputbuffer in bytes.[in] salt A salt or label, if supported by the encryption algorithm. If the algorithm does not support a salt, pass NULL. If the algorithm supports an optional salt and you do not want to pass a salt, passNULL.
- For PSA_ALG_RSA_PKCS1V15_CRYPT, no salt is supported.
- Parameters
-
salt_length Size of the saltbuffer in bytes. IfsaltisNULL, pass 0.[out] output Buffer where the encrypted message is to be written. output_size Size of the outputbuffer in bytes.[out] output_length On success, the number of bytes that make up the returned output.
- Return values
-
PSA_SUCCESS \emptydescription PSA_ERROR_BUFFER_TOO_SMALL The size of the outputbuffer is too small. You can determine a sufficient buffer size by calling PSA_ASYMMETRIC_ENCRYPT_OUTPUT_SIZE(key_type,key_bits,alg) wherekey_typeandkey_bitsare the type and bit-size respectively ofkey.PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_COMMUNICATION_FAILURE \emptydescription PSA_ERROR_HARDWARE_FAILURE \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_INSUFFICIENT_ENTROPY \emptydescription PSA_ERROR_BAD_STATE The library has not been previously initialized by psa_crypto_init(). It is implementation-dependent whether a failure to initialize results in this error code.
◆ mbedtls_psa_rsa_export_key()
| psa_status_t mbedtls_psa_rsa_export_key | ( | psa_key_type_t | type, |
| mbedtls_rsa_context * | rsa, | ||
| uint8_t * | data, | ||
| size_t | data_size, | ||
| size_t * | data_length | ||
| ) |
Export an RSA key to export representation
- Parameters
-
[in] type The type of key (public/private) to export [in] rsa The internal RSA representation from which to export [out] data The buffer to export to [in] data_size The length of the buffer to export to [out] data_length The amount of bytes written to data
◆ mbedtls_psa_rsa_export_public_key()
| psa_status_t mbedtls_psa_rsa_export_public_key | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| uint8_t * | data, | ||
| size_t | data_size, | ||
| size_t * | data_length | ||
| ) |
Export a public RSA key or the public part of an RSA key pair in binary format.
- Note
- The signature of this function is that of a PSA driver export_public_key entry point. This function behaves as an export_public_key entry point as defined in the PSA driver interface specification.
- Parameters
-
[in] attributes The attributes for the key to export. [in] key_buffer Material or context of the key to export. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[out] data Buffer where the key data is to be written. [in] data_size Size of the databuffer in bytes.[out] data_length On success, the number of bytes written in data.
- Return values
-
PSA_SUCCESS The RSA public key was exported successfully. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_COMMUNICATION_FAILURE \emptydescription PSA_ERROR_HARDWARE_FAILURE \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_STORAGE_FAILURE \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription
◆ mbedtls_psa_rsa_generate_key()
| psa_status_t mbedtls_psa_rsa_generate_key | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | custom_data, | ||
| size_t | custom_data_length, | ||
| uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| size_t * | key_buffer_length | ||
| ) |
Generate an RSA key.
- Parameters
-
[in] attributes The attributes for the RSA key to generate. [in] custom_data The public exponent to use. This can be a null pointer if params_data_lengthis 0.custom_data_length Length of custom_datain bytes. This can be 0, in which case the public exponent will be 65537.[out] key_buffer Buffer where the key data is to be written. [in] key_buffer_size Size of key_bufferin bytes.[out] key_buffer_length On success, the number of bytes written in key_buffer.
- Return values
-
PSA_SUCCESS The key was successfully generated. PSA_ERROR_NOT_SUPPORTED Key length or type not supported. PSA_ERROR_BUFFER_TOO_SMALL The size of key_bufferis too small.
◆ mbedtls_psa_rsa_import_key()
| psa_status_t mbedtls_psa_rsa_import_key | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | data, | ||
| size_t | data_length, | ||
| uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| size_t * | key_buffer_length, | ||
| size_t * | bits | ||
| ) |
Import an RSA key in binary format.
- Note
- The signature of this function is that of a PSA driver import_key entry point. This function behaves as an import_key entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes for the key to import. [in] data The buffer containing the key data in import format. [in] data_length Size of the databuffer in bytes.[out] key_buffer The buffer containing the key data in output format. [in] key_buffer_size Size of the key_bufferbuffer in bytes. This size is greater or equal todata_length.[out] key_buffer_length The length of the data written in key_bufferin bytes.[out] bits The key size in number of bits.
- Return values
-
PSA_SUCCESS The RSA key was imported successfully. PSA_ERROR_INVALID_ARGUMENT The key data is not correctly formatted. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription
◆ mbedtls_psa_rsa_load_representation()
| psa_status_t mbedtls_psa_rsa_load_representation | ( | psa_key_type_t | type, |
| const uint8_t * | data, | ||
| size_t | data_length, | ||
| mbedtls_rsa_context ** | p_rsa | ||
| ) |
Load the contents of a key buffer into an internal RSA representation
- Parameters
-
[in] type The type of key contained in data.[in] data The buffer from which to load the representation. [in] data_length The size in bytes of data.[out] p_rsa Returns a pointer to an RSA context on success. The caller is responsible for freeing both the contents of the context and the context itself when done.
◆ mbedtls_psa_rsa_sign_hash()
| psa_status_t mbedtls_psa_rsa_sign_hash | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | hash, | ||
| size_t | hash_length, | ||
| uint8_t * | signature, | ||
| size_t | signature_size, | ||
| size_t * | signature_length | ||
| ) |
Sign an already-calculated hash with an RSA private key.
- Note
- The signature of this function is that of a PSA driver sign_hash entry point. This function behaves as a sign_hash entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes of the RSA key to use for the operation. [in] key_buffer The buffer containing the RSA key context. format. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[in] alg A signature algorithm that is compatible with an RSA key. [in] hash The hash or message to sign. [in] hash_length Size of the hashbuffer in bytes.[out] signature Buffer where the signature is to be written. [in] signature_size Size of the signaturebuffer in bytes.[out] signature_length On success, the number of bytes that make up the returned signature value.
- Return values
-
PSA_SUCCESS \emptydescription PSA_ERROR_BUFFER_TOO_SMALL The size of the signaturebuffer is too small. You can determine a sufficient buffer size by calling PSA_SIGN_OUTPUT_SIZE(PSA_KEY_TYPE_RSA_KEY_PAIR,key_bits,alg) wherekey_bitsis the bit-size of the RSA key.PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription PSA_ERROR_CORRUPTION_DETECTED \emptydescription PSA_ERROR_INSUFFICIENT_ENTROPY \emptydescription
◆ mbedtls_psa_rsa_verify_hash()
| psa_status_t mbedtls_psa_rsa_verify_hash | ( | const psa_key_attributes_t * | attributes, |
| const uint8_t * | key_buffer, | ||
| size_t | key_buffer_size, | ||
| psa_algorithm_t | alg, | ||
| const uint8_t * | hash, | ||
| size_t | hash_length, | ||
| const uint8_t * | signature, | ||
| size_t | signature_length | ||
| ) |
Verify the signature a hash or short message using a public RSA key.
- Note
- The signature of this function is that of a PSA driver verify_hash entry point. This function behaves as a verify_hash entry point as defined in the PSA driver interface specification for transparent drivers.
- Parameters
-
[in] attributes The attributes of the RSA key to use for the operation. [in] key_buffer The buffer containing the RSA key context. format. [in] key_buffer_size Size of the key_bufferbuffer in bytes.[in] alg A signature algorithm that is compatible with an RSA key. [in] hash The hash or message whose signature is to be verified. [in] hash_length Size of the hashbuffer in bytes.[in] signature Buffer containing the signature to verify. [in] signature_length Size of the signaturebuffer in bytes.
- Return values
-
PSA_SUCCESS The signature is valid. PSA_ERROR_INVALID_SIGNATURE The calculation was performed successfully, but the passed signature is not a valid signature. PSA_ERROR_NOT_SUPPORTED \emptydescription PSA_ERROR_INVALID_ARGUMENT \emptydescription PSA_ERROR_INSUFFICIENT_MEMORY \emptydescription
