#include <x509_crl.h>
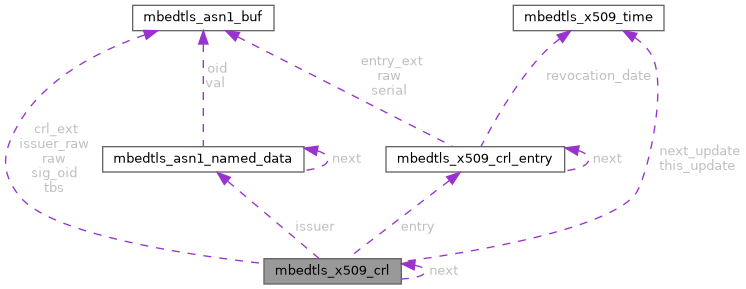
Public Member Functions | |
| mbedtls_x509_buf | MBEDTLS_PRIVATE (sig_oid2) |
| mbedtls_x509_buf | MBEDTLS_PRIVATE (sig) |
| mbedtls_md_type_t | MBEDTLS_PRIVATE (sig_md) |
| mbedtls_pk_type_t | MBEDTLS_PRIVATE (sig_pk) |
| void * | MBEDTLS_PRIVATE (sig_opts) |
Detailed Description
Certificate revocation list structure. Every CRL may have multiple entries.
Member Function Documentation
◆ MBEDTLS_PRIVATE() [1/5]
| mbedtls_x509_buf mbedtls_x509_crl::MBEDTLS_PRIVATE | ( | sig | ) |
◆ MBEDTLS_PRIVATE() [2/5]
| mbedtls_md_type_t mbedtls_x509_crl::MBEDTLS_PRIVATE | ( | sig_md | ) |
Internal representation of the MD algorithm of the signature algorithm, e.g. MBEDTLS_MD_SHA256
◆ MBEDTLS_PRIVATE() [3/5]
| mbedtls_x509_buf mbedtls_x509_crl::MBEDTLS_PRIVATE | ( | sig_oid2 | ) |
◆ MBEDTLS_PRIVATE() [4/5]
| void * mbedtls_x509_crl::MBEDTLS_PRIVATE | ( | sig_opts | ) |
Signature options to be passed to mbedtls_pk_verify_ext(), e.g. for RSASSA-PSS
◆ MBEDTLS_PRIVATE() [5/5]
| mbedtls_pk_type_t mbedtls_x509_crl::MBEDTLS_PRIVATE | ( | sig_pk | ) |
Internal representation of the Public Key algorithm of the signature algorithm, e.g. MBEDTLS_PK_RSA
Member Data Documentation
◆ crl_ext
| mbedtls_x509_buf mbedtls_x509_crl::crl_ext |
◆ entry
| mbedtls_x509_crl_entry mbedtls_x509_crl::entry |
The CRL entries containing the certificate revocation times for this CA.
◆ issuer
| mbedtls_x509_name mbedtls_x509_crl::issuer |
The parsed issuer data (named information object).
◆ issuer_raw
| mbedtls_x509_buf mbedtls_x509_crl::issuer_raw |
The raw issuer data (DER).
◆ next
| struct mbedtls_x509_crl* mbedtls_x509_crl::next |
Next element in the linked list of CRL. NULL indicates the end of the list. Do not modify this field directly.
◆ next_update
| mbedtls_x509_time mbedtls_x509_crl::next_update |
◆ raw
| mbedtls_x509_buf mbedtls_x509_crl::raw |
The raw certificate data (DER).
◆ sig_oid
| mbedtls_x509_buf mbedtls_x509_crl::sig_oid |
CRL signature type identifier
◆ tbs
| mbedtls_x509_buf mbedtls_x509_crl::tbs |
The raw certificate body (DER). The part that is To Be Signed.
◆ this_update
| mbedtls_x509_time mbedtls_x509_crl::this_update |
◆ version
| int mbedtls_x509_crl::version |
CRL version (1=v1, 2=v2)
The documentation for this struct was generated from the following file:
- XenevaOS/Ports/mbedtls/include/mbedtls/x509_crl.h
