X.509 generic defines and structures. More...
#include "mbedtls/private_access.h"#include "mbedtls/build_info.h"#include "mbedtls/asn1.h"#include "mbedtls/pk.h"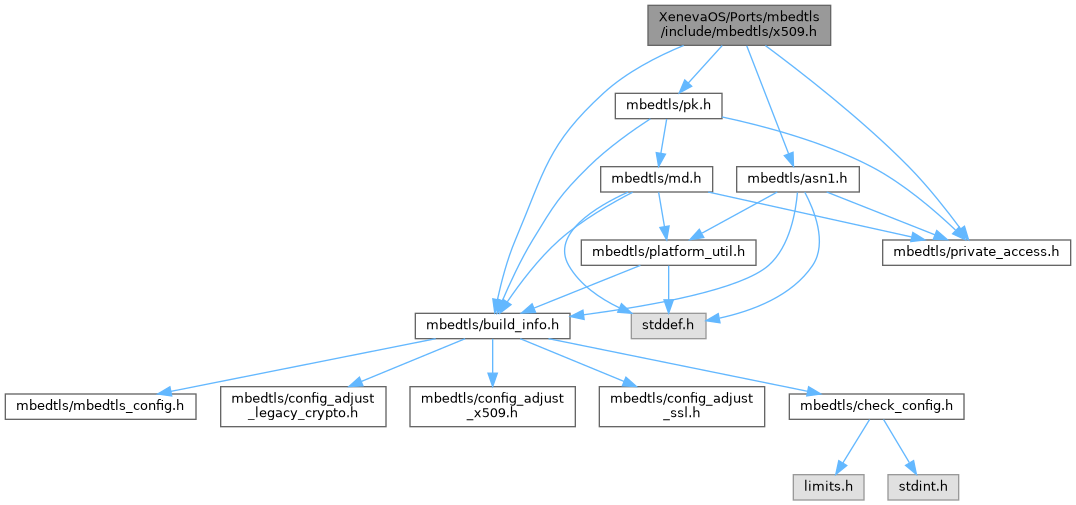
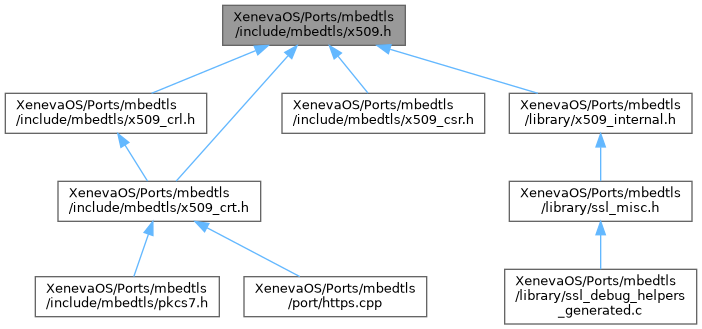
Go to the source code of this file.
Classes | |
| struct | mbedtls_x509_authority |
| struct | mbedtls_x509_time |
| struct | mbedtls_x509_san_other_name |
| struct | mbedtls_x509_subject_alternative_name |
| struct | mbedtls_x509_san_list |
Typedefs | |
Structures for parsing X.509 certificates, CRLs and CSRs | |
| typedef mbedtls_asn1_buf | mbedtls_x509_buf |
| typedef mbedtls_asn1_bitstring | mbedtls_x509_bitstring |
| typedef mbedtls_asn1_named_data | mbedtls_x509_name |
| typedef mbedtls_asn1_sequence | mbedtls_x509_sequence |
| typedef struct mbedtls_x509_authority | mbedtls_x509_authority |
| typedef struct mbedtls_x509_time | mbedtls_x509_time |
| typedef struct mbedtls_x509_san_other_name | mbedtls_x509_san_other_name |
| typedef struct mbedtls_x509_subject_alternative_name | mbedtls_x509_subject_alternative_name |
| typedef struct mbedtls_x509_san_list | mbedtls_x509_san_list |
Functions | |
| int | mbedtls_x509_dn_gets (char *buf, size_t size, const mbedtls_x509_name *dn) |
| Store the certificate DN in printable form into buf; no more than size characters will be written. | |
| int | mbedtls_x509_string_to_names (mbedtls_asn1_named_data **head, const char *name) |
Convert the certificate DN string name into a linked list of mbedtls_x509_name (equivalent to mbedtls_asn1_named_data). | |
| int | mbedtls_x509_serial_gets (char *buf, size_t size, const mbedtls_x509_buf *serial) |
| Store the certificate serial in printable form into buf; no more than size characters will be written. | |
| int | mbedtls_x509_time_cmp (const mbedtls_x509_time *t1, const mbedtls_x509_time *t2) |
| Compare pair of mbedtls_x509_time. | |
| int | mbedtls_x509_time_is_past (const mbedtls_x509_time *to) |
| Check a given mbedtls_x509_time against the system time and tell if it's in the past. | |
| int | mbedtls_x509_time_is_future (const mbedtls_x509_time *from) |
| Check a given mbedtls_x509_time against the system time and tell if it's in the future. | |
| int | mbedtls_x509_parse_subject_alt_name (const mbedtls_x509_buf *san_buf, mbedtls_x509_subject_alternative_name *san) |
| This function parses an item in the SubjectAlternativeNames extension. Please note that this function might allocate additional memory for a subject alternative name, thus mbedtls_x509_free_subject_alt_name has to be called to dispose of this additional memory afterwards. | |
| void | mbedtls_x509_free_subject_alt_name (mbedtls_x509_subject_alternative_name *san) |
| Unallocate all data related to subject alternative name. | |
| size_t | mbedtls_x509_crt_parse_cn_inet_pton (const char *cn, void *dst) |
| This function parses a CN string as an IP address. | |
Detailed Description
X.509 generic defines and structures.
Internal part of the public "x509.h".
Macro Definition Documentation
◆ MBEDTLS_X509_EXT_AUTHORITY_KEY_IDENTIFIER
| #define MBEDTLS_X509_EXT_AUTHORITY_KEY_IDENTIFIER MBEDTLS_OID_X509_EXT_AUTHORITY_KEY_IDENTIFIER |
◆ MBEDTLS_X509_EXT_BASIC_CONSTRAINTS
| #define MBEDTLS_X509_EXT_BASIC_CONSTRAINTS MBEDTLS_OID_X509_EXT_BASIC_CONSTRAINTS /* Supported */ |
◆ MBEDTLS_X509_EXT_CERTIFICATE_POLICIES
| #define MBEDTLS_X509_EXT_CERTIFICATE_POLICIES MBEDTLS_OID_X509_EXT_CERTIFICATE_POLICIES |
◆ MBEDTLS_X509_EXT_CRL_DISTRIBUTION_POINTS
| #define MBEDTLS_X509_EXT_CRL_DISTRIBUTION_POINTS MBEDTLS_OID_X509_EXT_CRL_DISTRIBUTION_POINTS |
◆ MBEDTLS_X509_EXT_EXTENDED_KEY_USAGE
| #define MBEDTLS_X509_EXT_EXTENDED_KEY_USAGE MBEDTLS_OID_X509_EXT_EXTENDED_KEY_USAGE |
◆ MBEDTLS_X509_EXT_FRESHEST_CRL
| #define MBEDTLS_X509_EXT_FRESHEST_CRL MBEDTLS_OID_X509_EXT_FRESHEST_CRL |
◆ MBEDTLS_X509_EXT_INIHIBIT_ANYPOLICY
| #define MBEDTLS_X509_EXT_INIHIBIT_ANYPOLICY MBEDTLS_OID_X509_EXT_INIHIBIT_ANYPOLICY |
◆ MBEDTLS_X509_EXT_ISSUER_ALT_NAME
| #define MBEDTLS_X509_EXT_ISSUER_ALT_NAME MBEDTLS_OID_X509_EXT_ISSUER_ALT_NAME |
◆ MBEDTLS_X509_EXT_KEY_USAGE
| #define MBEDTLS_X509_EXT_KEY_USAGE MBEDTLS_OID_X509_EXT_KEY_USAGE |
◆ MBEDTLS_X509_EXT_NAME_CONSTRAINTS
| #define MBEDTLS_X509_EXT_NAME_CONSTRAINTS MBEDTLS_OID_X509_EXT_NAME_CONSTRAINTS |
◆ MBEDTLS_X509_EXT_NS_CERT_TYPE
| #define MBEDTLS_X509_EXT_NS_CERT_TYPE MBEDTLS_OID_X509_EXT_NS_CERT_TYPE |
◆ MBEDTLS_X509_EXT_POLICY_CONSTRAINTS
| #define MBEDTLS_X509_EXT_POLICY_CONSTRAINTS MBEDTLS_OID_X509_EXT_POLICY_CONSTRAINTS |
◆ MBEDTLS_X509_EXT_POLICY_MAPPINGS
| #define MBEDTLS_X509_EXT_POLICY_MAPPINGS MBEDTLS_OID_X509_EXT_POLICY_MAPPINGS |
◆ MBEDTLS_X509_EXT_SUBJECT_ALT_NAME
| #define MBEDTLS_X509_EXT_SUBJECT_ALT_NAME MBEDTLS_OID_X509_EXT_SUBJECT_ALT_NAME /* Supported (DNS) */ |
◆ MBEDTLS_X509_EXT_SUBJECT_DIRECTORY_ATTRS
| #define MBEDTLS_X509_EXT_SUBJECT_DIRECTORY_ATTRS MBEDTLS_OID_X509_EXT_SUBJECT_DIRECTORY_ATTRS |
◆ MBEDTLS_X509_EXT_SUBJECT_KEY_IDENTIFIER
| #define MBEDTLS_X509_EXT_SUBJECT_KEY_IDENTIFIER MBEDTLS_OID_X509_EXT_SUBJECT_KEY_IDENTIFIER |
◆ MBEDTLS_X509_FORMAT_DER
| #define MBEDTLS_X509_FORMAT_DER 1 |
◆ MBEDTLS_X509_FORMAT_PEM
| #define MBEDTLS_X509_FORMAT_PEM 2 |
◆ MBEDTLS_X509_KU_CRL_SIGN
| #define MBEDTLS_X509_KU_CRL_SIGN (0x02) /* bit 6 */ |
◆ MBEDTLS_X509_KU_DATA_ENCIPHERMENT
| #define MBEDTLS_X509_KU_DATA_ENCIPHERMENT (0x10) /* bit 3 */ |
◆ MBEDTLS_X509_KU_DECIPHER_ONLY
| #define MBEDTLS_X509_KU_DECIPHER_ONLY (0x8000) /* bit 8 */ |
◆ MBEDTLS_X509_KU_DIGITAL_SIGNATURE
| #define MBEDTLS_X509_KU_DIGITAL_SIGNATURE (0x80) /* bit 0 */ |
◆ MBEDTLS_X509_KU_ENCIPHER_ONLY
| #define MBEDTLS_X509_KU_ENCIPHER_ONLY (0x01) /* bit 7 */ |
◆ MBEDTLS_X509_KU_KEY_AGREEMENT
| #define MBEDTLS_X509_KU_KEY_AGREEMENT (0x08) /* bit 4 */ |
◆ MBEDTLS_X509_KU_KEY_CERT_SIGN
| #define MBEDTLS_X509_KU_KEY_CERT_SIGN (0x04) /* bit 5 */ |
◆ MBEDTLS_X509_KU_KEY_ENCIPHERMENT
| #define MBEDTLS_X509_KU_KEY_ENCIPHERMENT (0x20) /* bit 2 */ |
◆ MBEDTLS_X509_KU_NON_REPUDIATION
| #define MBEDTLS_X509_KU_NON_REPUDIATION (0x40) /* bit 1 */ |
◆ MBEDTLS_X509_MAX_DN_NAME_SIZE
| #define MBEDTLS_X509_MAX_DN_NAME_SIZE 256 |
Maximum value size of a DN entry
◆ MBEDTLS_X509_NS_CERT_TYPE_EMAIL
| #define MBEDTLS_X509_NS_CERT_TYPE_EMAIL (0x20) /* bit 2 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_EMAIL_CA
| #define MBEDTLS_X509_NS_CERT_TYPE_EMAIL_CA (0x02) /* bit 6 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_OBJECT_SIGNING
| #define MBEDTLS_X509_NS_CERT_TYPE_OBJECT_SIGNING (0x10) /* bit 3 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_OBJECT_SIGNING_CA
| #define MBEDTLS_X509_NS_CERT_TYPE_OBJECT_SIGNING_CA (0x01) /* bit 7 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_RESERVED
| #define MBEDTLS_X509_NS_CERT_TYPE_RESERVED (0x08) /* bit 4 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_SSL_CA
| #define MBEDTLS_X509_NS_CERT_TYPE_SSL_CA (0x04) /* bit 5 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_SSL_CLIENT
| #define MBEDTLS_X509_NS_CERT_TYPE_SSL_CLIENT (0x80) /* bit 0 */ |
◆ MBEDTLS_X509_NS_CERT_TYPE_SSL_SERVER
| #define MBEDTLS_X509_NS_CERT_TYPE_SSL_SERVER (0x40) /* bit 1 */ |
◆ MBEDTLS_X509_SAFE_SNPRINTF
| #define MBEDTLS_X509_SAFE_SNPRINTF |
◆ MBEDTLS_X509_SAN_DIRECTORY_NAME
| #define MBEDTLS_X509_SAN_DIRECTORY_NAME 4 |
◆ MBEDTLS_X509_SAN_DNS_NAME
| #define MBEDTLS_X509_SAN_DNS_NAME 2 |
◆ MBEDTLS_X509_SAN_EDI_PARTY_NAME
| #define MBEDTLS_X509_SAN_EDI_PARTY_NAME 5 |
◆ MBEDTLS_X509_SAN_IP_ADDRESS
| #define MBEDTLS_X509_SAN_IP_ADDRESS 7 |
◆ MBEDTLS_X509_SAN_OTHER_NAME
| #define MBEDTLS_X509_SAN_OTHER_NAME 0 |
◆ MBEDTLS_X509_SAN_REGISTERED_ID
| #define MBEDTLS_X509_SAN_REGISTERED_ID 8 |
◆ MBEDTLS_X509_SAN_RFC822_NAME
| #define MBEDTLS_X509_SAN_RFC822_NAME 1 |
◆ MBEDTLS_X509_SAN_UNIFORM_RESOURCE_IDENTIFIER
| #define MBEDTLS_X509_SAN_UNIFORM_RESOURCE_IDENTIFIER 6 |
◆ MBEDTLS_X509_SAN_X400_ADDRESS_NAME
| #define MBEDTLS_X509_SAN_X400_ADDRESS_NAME 3 |
Function Documentation
◆ mbedtls_x509_crt_parse_cn_inet_pton()
| size_t mbedtls_x509_crt_parse_cn_inet_pton | ( | const char * | cn, |
| void * | dst | ||
| ) |
This function parses a CN string as an IP address.
- Parameters
-
cn The CN string to parse. CN string MUST be null-terminated. dst The target buffer to populate with the binary IP address. The buffer MUST be 16 bytes to save IPv6, and should be 4-byte aligned if the result will be used as struct in_addr. e.g. uint32_t dst[4]
- Note
cnis parsed as an IPv6 address if string contains ':', elsecnis parsed as an IPv4 address.
- Returns
- Length of binary IP address; num bytes written to target.
-
0on failure to parse CN string as an IP address.
◆ mbedtls_x509_dn_gets()
| int mbedtls_x509_dn_gets | ( | char * | buf, |
| size_t | size, | ||
| const mbedtls_x509_name * | dn | ||
| ) |
Store the certificate DN in printable form into buf; no more than size characters will be written.
- Parameters
-
buf Buffer to write to size Maximum size of buffer dn The X509 name to represent
- Returns
- The length of the string written (not including the terminated nul byte), or a negative error code.
◆ mbedtls_x509_free_subject_alt_name()
| void mbedtls_x509_free_subject_alt_name | ( | mbedtls_x509_subject_alternative_name * | san | ) |
Unallocate all data related to subject alternative name.
- Parameters
-
san SAN structure - extra memory owned by this structure will be freed
◆ mbedtls_x509_parse_subject_alt_name()
| int mbedtls_x509_parse_subject_alt_name | ( | const mbedtls_x509_buf * | san_buf, |
| mbedtls_x509_subject_alternative_name * | san | ||
| ) |
This function parses an item in the SubjectAlternativeNames extension. Please note that this function might allocate additional memory for a subject alternative name, thus mbedtls_x509_free_subject_alt_name has to be called to dispose of this additional memory afterwards.
- Parameters
-
san_buf The buffer holding the raw data item of the subject alternative name. san The target structure to populate with the parsed presentation of the subject alternative name encoded in san_buf.
- Note
- Supported GeneralName types, as defined in RFC 5280: "rfc822Name", "dnsName", "directoryName", "uniformResourceIdentifier" and "hardware_module_name" of type "otherName", as defined in RFC 4108.
-
This function should be called on a single raw data of subject alternative name. For example, after successful certificate parsing, one must iterate on every item in the
crt->subject_alt_namessequence, and pass it to this function.
- Warning
- The target structure contains pointers to the raw data of the parsed certificate, and its lifetime is restricted by the lifetime of the certificate.
- Returns
0on success- MBEDTLS_ERR_X509_FEATURE_UNAVAILABLE for an unsupported SAN type.
- Another negative value for any other failure.
◆ mbedtls_x509_serial_gets()
| int mbedtls_x509_serial_gets | ( | char * | buf, |
| size_t | size, | ||
| const mbedtls_x509_buf * | serial | ||
| ) |
Store the certificate serial in printable form into buf; no more than size characters will be written.
- Parameters
-
buf Buffer to write to size Maximum size of buffer serial The X509 serial to represent
- Returns
- The length of the string written (not including the terminated nul byte), or a negative error code.
◆ mbedtls_x509_string_to_names()
| int mbedtls_x509_string_to_names | ( | mbedtls_asn1_named_data ** | head, |
| const char * | name | ||
| ) |
Convert the certificate DN string name into a linked list of mbedtls_x509_name (equivalent to mbedtls_asn1_named_data).
- Note
- This function allocates a linked list, and places the head pointer in
head. This list must later be freed by a call to mbedtls_asn1_free_named_data_list().
- Parameters
-
[out] head Address in which to store the pointer to the head of the allocated list of mbedtls_x509_name. Must point to NULL on entry. [in] name The string representation of a DN to convert
- Returns
- 0 on success, or a negative error code.
◆ mbedtls_x509_time_cmp()
| int mbedtls_x509_time_cmp | ( | const mbedtls_x509_time * | t1, |
| const mbedtls_x509_time * | t2 | ||
| ) |
Compare pair of mbedtls_x509_time.
- Parameters
-
t1 mbedtls_x509_time to compare t2 mbedtls_x509_time to compare
- Returns
- < 0 if t1 is before t2 0 if t1 equals t2 > 0 if t1 is after t2
◆ mbedtls_x509_time_is_future()
| int mbedtls_x509_time_is_future | ( | const mbedtls_x509_time * | from | ) |
Check a given mbedtls_x509_time against the system time and tell if it's in the future.
- Note
- Intended usage is "if( is_future( valid_from ) ) ERROR". Hence the return value of 1 if on internal errors.
- Parameters
-
from mbedtls_x509_time to check
- Returns
- 1 if the given time is in the future or an error occurred, 0 otherwise.
◆ mbedtls_x509_time_is_past()
| int mbedtls_x509_time_is_past | ( | const mbedtls_x509_time * | to | ) |
Check a given mbedtls_x509_time against the system time and tell if it's in the past.
- Note
- Intended usage is "if( is_past( valid_to ) ) ERROR". Hence the return value of 1 if on internal errors.
- Parameters
-
to mbedtls_x509_time to check
- Returns
- 1 if the given time is in the past or an error occurred, 0 otherwise.
