PKCS #7 generic defines and structures https://tools.ietf.org/html/rfc2315. More...
#include "mbedtls/private_access.h"#include "mbedtls/build_info.h"#include "mbedtls/asn1.h"#include "mbedtls/x509_crt.h"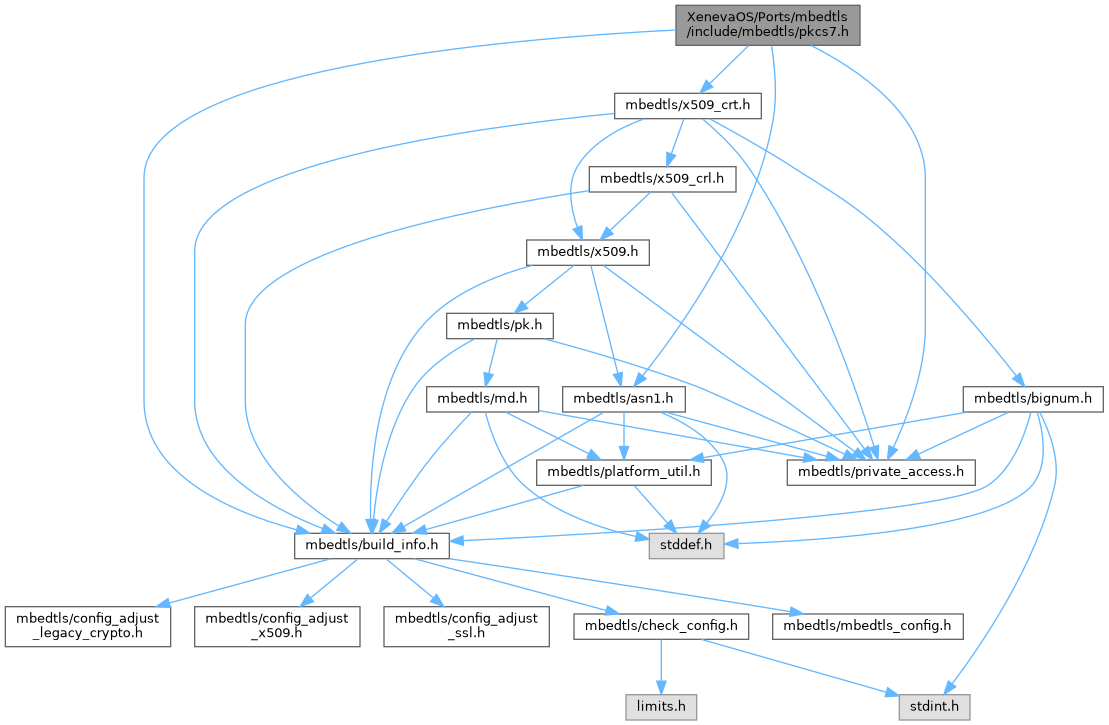
Go to the source code of this file.
Classes | |
| struct | mbedtls_pkcs7_signer_info |
| struct | mbedtls_pkcs7_signed_data |
| struct | mbedtls_pkcs7 |
Macros | |
PKCS #7 Module Error codes | |
Note: For the time being, this implementation of the PKCS #7 cryptographic message syntax is a partial implementation of RFC 2315. Differences include:
| |
| #define | MBEDTLS_ERR_PKCS7_INVALID_FORMAT -0x5300 |
| #define | MBEDTLS_ERR_PKCS7_FEATURE_UNAVAILABLE -0x5380 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_VERSION -0x5400 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_CONTENT_INFO -0x5480 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_ALG -0x5500 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_CERT -0x5580 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_SIGNATURE -0x5600 |
| #define | MBEDTLS_ERR_PKCS7_INVALID_SIGNER_INFO -0x5680 |
| #define | MBEDTLS_ERR_PKCS7_BAD_INPUT_DATA -0x5700 |
| #define | MBEDTLS_ERR_PKCS7_ALLOC_FAILED -0x5780 |
| #define | MBEDTLS_ERR_PKCS7_VERIFY_FAIL -0x5800 |
| #define | MBEDTLS_ERR_PKCS7_CERT_DATE_INVALID -0x5880 |
Detailed Description
PKCS #7 generic defines and structures https://tools.ietf.org/html/rfc2315.
Macro Definition Documentation
◆ MBEDTLS_ERR_PKCS7_ALLOC_FAILED
| #define MBEDTLS_ERR_PKCS7_ALLOC_FAILED -0x5780 |
Allocation of memory failed.
◆ MBEDTLS_ERR_PKCS7_BAD_INPUT_DATA
| #define MBEDTLS_ERR_PKCS7_BAD_INPUT_DATA -0x5700 |
Input invalid.
◆ MBEDTLS_ERR_PKCS7_CERT_DATE_INVALID
| #define MBEDTLS_ERR_PKCS7_CERT_DATE_INVALID -0x5880 |
The PKCS #7 date issued/expired dates are invalid
◆ MBEDTLS_ERR_PKCS7_FEATURE_UNAVAILABLE
| #define MBEDTLS_ERR_PKCS7_FEATURE_UNAVAILABLE -0x5380 |
Unavailable feature, e.g. anything other than signed data.
◆ MBEDTLS_ERR_PKCS7_INVALID_ALG
| #define MBEDTLS_ERR_PKCS7_INVALID_ALG -0x5500 |
The algorithm tag or value is invalid or cannot be parsed.
◆ MBEDTLS_ERR_PKCS7_INVALID_CERT
| #define MBEDTLS_ERR_PKCS7_INVALID_CERT -0x5580 |
The certificate tag or value is invalid or cannot be parsed.
◆ MBEDTLS_ERR_PKCS7_INVALID_CONTENT_INFO
| #define MBEDTLS_ERR_PKCS7_INVALID_CONTENT_INFO -0x5480 |
The PKCS #7 content info is invalid or cannot be parsed.
◆ MBEDTLS_ERR_PKCS7_INVALID_FORMAT
| #define MBEDTLS_ERR_PKCS7_INVALID_FORMAT -0x5300 |
The format is invalid, e.g. different type expected.
◆ MBEDTLS_ERR_PKCS7_INVALID_SIGNATURE
| #define MBEDTLS_ERR_PKCS7_INVALID_SIGNATURE -0x5600 |
Error parsing the signature
◆ MBEDTLS_ERR_PKCS7_INVALID_SIGNER_INFO
| #define MBEDTLS_ERR_PKCS7_INVALID_SIGNER_INFO -0x5680 |
Error parsing the signer's info
◆ MBEDTLS_ERR_PKCS7_INVALID_VERSION
| #define MBEDTLS_ERR_PKCS7_INVALID_VERSION -0x5400 |
The PKCS #7 version element is invalid or cannot be parsed.
◆ MBEDTLS_ERR_PKCS7_VERIFY_FAIL
| #define MBEDTLS_ERR_PKCS7_VERIFY_FAIL -0x5800 |
Verification Failed
◆ MBEDTLS_PKCS7_SUPPORTED_VERSION
| #define MBEDTLS_PKCS7_SUPPORTED_VERSION 0x01 |
Typedef Documentation
◆ mbedtls_pkcs7
| typedef struct mbedtls_pkcs7 mbedtls_pkcs7 |
Structure holding PKCS #7 structure, only signed data for now
◆ mbedtls_pkcs7_buf
| typedef mbedtls_asn1_buf mbedtls_pkcs7_buf |
Type-length-value structure that allows for ASN.1 using DER.
◆ mbedtls_pkcs7_name
Container for ASN.1 named information objects. It allows for Relative Distinguished Names (e.g. cn=localhost,ou=code,etc.).
◆ mbedtls_pkcs7_sequence
Container for a sequence of ASN.1 items
◆ mbedtls_pkcs7_signed_data
| typedef struct mbedtls_pkcs7_signed_data mbedtls_pkcs7_signed_data |
Structure holding the signed data section
◆ mbedtls_pkcs7_signer_info
| typedef struct mbedtls_pkcs7_signer_info mbedtls_pkcs7_signer_info |
Structure holding PKCS #7 signer info
Enumeration Type Documentation
◆ mbedtls_pkcs7_type
| enum mbedtls_pkcs7_type |
Function Documentation
◆ mbedtls_pkcs7_free()
| void mbedtls_pkcs7_free | ( | mbedtls_pkcs7 * | pkcs7 | ) |
Unallocate all PKCS #7 data and zeroize the memory. It doesn't free pkcs7 itself. This should be done by the caller.
- Parameters
-
pkcs7 mbedtls_pkcs7 structure to free.
◆ mbedtls_pkcs7_init()
| void mbedtls_pkcs7_init | ( | mbedtls_pkcs7 * | pkcs7 | ) |
Initialize mbedtls_pkcs7 structure.
- Parameters
-
pkcs7 mbedtls_pkcs7 structure.
◆ mbedtls_pkcs7_parse_der()
| int mbedtls_pkcs7_parse_der | ( | mbedtls_pkcs7 * | pkcs7, |
| const unsigned char * | buf, | ||
| const size_t | buflen | ||
| ) |
Parse a single DER formatted PKCS #7 detached signature.
- Parameters
-
pkcs7 The mbedtls_pkcs7 structure to be filled by the parser. buf The buffer holding only the DER encoded PKCS #7 content. buflen The size in bytes of buf. The size must be exactly the length of the DER encoded PKCS #7 content.
- Note
- This function makes an internal copy of the PKCS #7 buffer
buf. In particular,bufmay be destroyed or reused after this call returns. - Signatures with internal data are not supported.
- Returns
- The
mbedtls_pkcs7_typeofbuf, if successful. - A negative error code on failure.
◆ mbedtls_pkcs7_signed_data_verify()
| int mbedtls_pkcs7_signed_data_verify | ( | mbedtls_pkcs7 * | pkcs7, |
| const mbedtls_x509_crt * | cert, | ||
| const unsigned char * | data, | ||
| size_t | datalen | ||
| ) |
Verification of PKCS #7 signature against a caller-supplied certificate.
For each signer in the PKCS structure, this function computes a signature over the supplied data, using the supplied certificate and the same digest algorithm as specified by the signer. It then compares this signature against the signer's signature; verification succeeds if any comparison matches.
This function does not use the certificates held within the PKCS #7 structure itself, and does not check that the certificate is signed by a trusted certification authority.
- Parameters
-
pkcs7 mbedtls_pkcs7 structure containing signature. cert Certificate containing key to verify signature. data Plain data on which signature has to be verified. datalen Length of the data.
- Note
- This function internally calculates the hash on the supplied plain data for signature verification.
- Returns
- 0 if the signature verifies, or a negative error code on failure.
◆ mbedtls_pkcs7_signed_hash_verify()
| int mbedtls_pkcs7_signed_hash_verify | ( | mbedtls_pkcs7 * | pkcs7, |
| const mbedtls_x509_crt * | cert, | ||
| const unsigned char * | hash, | ||
| size_t | hashlen | ||
| ) |
Verification of PKCS #7 signature against a caller-supplied certificate.
For each signer in the PKCS structure, this function validates a signature over the supplied hash, using the supplied certificate and the same digest algorithm as specified by the signer. Verification succeeds if any signature is good.
This function does not use the certificates held within the PKCS #7 structure itself, and does not check that the certificate is signed by a trusted certification authority.
- Parameters
-
pkcs7 PKCS #7 structure containing signature. cert Certificate containing key to verify signature. hash Hash of the plain data on which signature has to be verified. hashlen Length of the hash.
- Note
- This function is different from mbedtls_pkcs7_signed_data_verify() in that it is directly passed the hash of the data.
- Returns
- 0 if the signature verifies, or a negative error code on failure.
