#include <x509_crt.h>
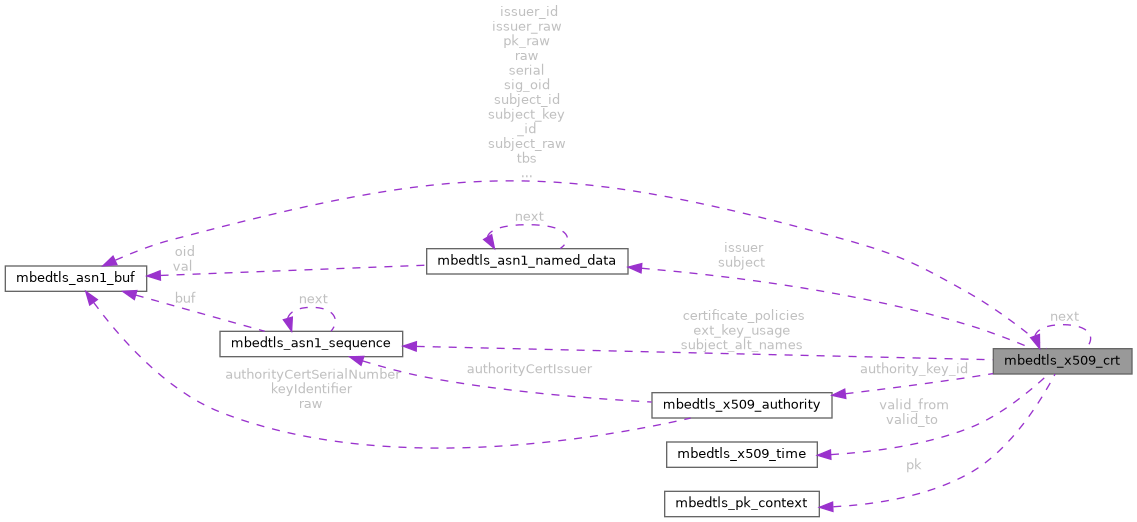
Public Member Functions | |
| int | MBEDTLS_PRIVATE (own_buffer) |
| int | MBEDTLS_PRIVATE (ext_types) |
| int | MBEDTLS_PRIVATE (ca_istrue) |
| int | MBEDTLS_PRIVATE (max_pathlen) |
| unsigned int | MBEDTLS_PRIVATE (key_usage) |
| unsigned char | MBEDTLS_PRIVATE (ns_cert_type) |
| mbedtls_x509_buf | MBEDTLS_PRIVATE (sig) |
| mbedtls_md_type_t | MBEDTLS_PRIVATE (sig_md) |
| mbedtls_pk_type_t | MBEDTLS_PRIVATE (sig_pk) |
| void * | MBEDTLS_PRIVATE (sig_opts) |
Detailed Description
Container for an X.509 certificate. The certificate may be chained.
Some fields of this structure are publicly readable. Do not modify them except via Mbed TLS library functions: the effect of modifying those fields or the data that those fields points to is unspecified.
Member Function Documentation
◆ MBEDTLS_PRIVATE() [1/10]
| int mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | ca_istrue | ) |
Optional Basic Constraint extension value: 1 if this certificate belongs to a CA, 0 otherwise.
◆ MBEDTLS_PRIVATE() [2/10]
| int mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | ext_types | ) |
Bit string containing detected and parsed extensions
◆ MBEDTLS_PRIVATE() [3/10]
| unsigned int mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | key_usage | ) |
Optional key usage extension value: See the values in x509.h
◆ MBEDTLS_PRIVATE() [4/10]
| int mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | max_pathlen | ) |
Optional Basic Constraint extension value: The maximum path length to the root certificate. Path length is 1 higher than RFC 5280 'meaning', so 1+
◆ MBEDTLS_PRIVATE() [5/10]
| unsigned char mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | ns_cert_type | ) |
Optional Netscape certificate type extension value: See the values in x509.h
◆ MBEDTLS_PRIVATE() [6/10]
| int mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | own_buffer | ) |
Indicates if raw is owned by the structure or not.
◆ MBEDTLS_PRIVATE() [7/10]
| mbedtls_x509_buf mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | sig | ) |
Signature: hash of the tbs part signed with the private key.
◆ MBEDTLS_PRIVATE() [8/10]
| mbedtls_md_type_t mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | sig_md | ) |
Internal representation of the MD algorithm of the signature algorithm, e.g. MBEDTLS_MD_SHA256
◆ MBEDTLS_PRIVATE() [9/10]
| void * mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | sig_opts | ) |
Signature options to be passed to mbedtls_pk_verify_ext(), e.g. for RSASSA-PSS
◆ MBEDTLS_PRIVATE() [10/10]
| mbedtls_pk_type_t mbedtls_x509_crt::MBEDTLS_PRIVATE | ( | sig_pk | ) |
Internal representation of the Public Key algorithm of the signature algorithm, e.g. MBEDTLS_PK_RSA
Member Data Documentation
◆ authority_key_id
| mbedtls_x509_authority mbedtls_x509_crt::authority_key_id |
Optional X.509 v3 extension authority key identifier.
◆ certificate_policies
| mbedtls_x509_sequence mbedtls_x509_crt::certificate_policies |
Optional list of certificate policies (Only anyPolicy is printed and enforced, however the rest of the policies are still listed).
◆ ext_key_usage
| mbedtls_x509_sequence mbedtls_x509_crt::ext_key_usage |
Optional list of extended key usage OIDs.
◆ issuer
| mbedtls_x509_name mbedtls_x509_crt::issuer |
The parsed issuer data (named information object).
◆ issuer_id
| mbedtls_x509_buf mbedtls_x509_crt::issuer_id |
Optional X.509 v2/v3 issuer unique identifier.
◆ issuer_raw
| mbedtls_x509_buf mbedtls_x509_crt::issuer_raw |
The raw issuer data (DER). Used for quick comparison.
◆ next
| struct mbedtls_x509_crt* mbedtls_x509_crt::next |
Next certificate in the linked list that constitutes the CA chain. NULL indicates the end of the list. Do not modify this field directly.
◆ pk
| mbedtls_pk_context mbedtls_x509_crt::pk |
Container for the public key context.
◆ pk_raw
| mbedtls_x509_buf mbedtls_x509_crt::pk_raw |
◆ raw
| mbedtls_x509_buf mbedtls_x509_crt::raw |
The raw certificate data (DER).
◆ serial
| mbedtls_x509_buf mbedtls_x509_crt::serial |
Unique id for certificate issued by a specific CA.
◆ sig_oid
| mbedtls_x509_buf mbedtls_x509_crt::sig_oid |
Signature algorithm, e.g. sha1RSA
◆ subject
| mbedtls_x509_name mbedtls_x509_crt::subject |
The parsed subject data (named information object).
◆ subject_alt_names
| mbedtls_x509_sequence mbedtls_x509_crt::subject_alt_names |
Optional list of raw entries of Subject Alternative Names extension. These can be later parsed by mbedtls_x509_parse_subject_alt_name.
◆ subject_id
| mbedtls_x509_buf mbedtls_x509_crt::subject_id |
Optional X.509 v2/v3 subject unique identifier.
◆ subject_key_id
| mbedtls_x509_buf mbedtls_x509_crt::subject_key_id |
Optional X.509 v3 extension subject key identifier.
◆ subject_raw
| mbedtls_x509_buf mbedtls_x509_crt::subject_raw |
The raw subject data (DER). Used for quick comparison.
◆ tbs
| mbedtls_x509_buf mbedtls_x509_crt::tbs |
The raw certificate body (DER). The part that is To Be Signed.
◆ v3_ext
| mbedtls_x509_buf mbedtls_x509_crt::v3_ext |
Optional X.509 v3 extensions.
◆ valid_from
| mbedtls_x509_time mbedtls_x509_crt::valid_from |
Start time of certificate validity.
◆ valid_to
| mbedtls_x509_time mbedtls_x509_crt::valid_to |
End time of certificate validity.
◆ version
| int mbedtls_x509_crt::version |
The X.509 version. (1=v1, 2=v2, 3=v3)
The documentation for this struct was generated from the following file:
- XenevaOS/Ports/mbedtls/include/mbedtls/x509_crt.h
