Internal functions shared by the SSL modules. More...
#include "mbedtls/build_info.h"#include "common.h"#include "mbedtls/error.h"#include "mbedtls/ssl.h"#include "mbedtls/debug.h"#include "debug_internal.h"#include "mbedtls/cipher.h"#include "mbedtls/pk.h"#include "ssl_ciphersuites_internal.h"#include "x509_internal.h"#include "pk_internal.h"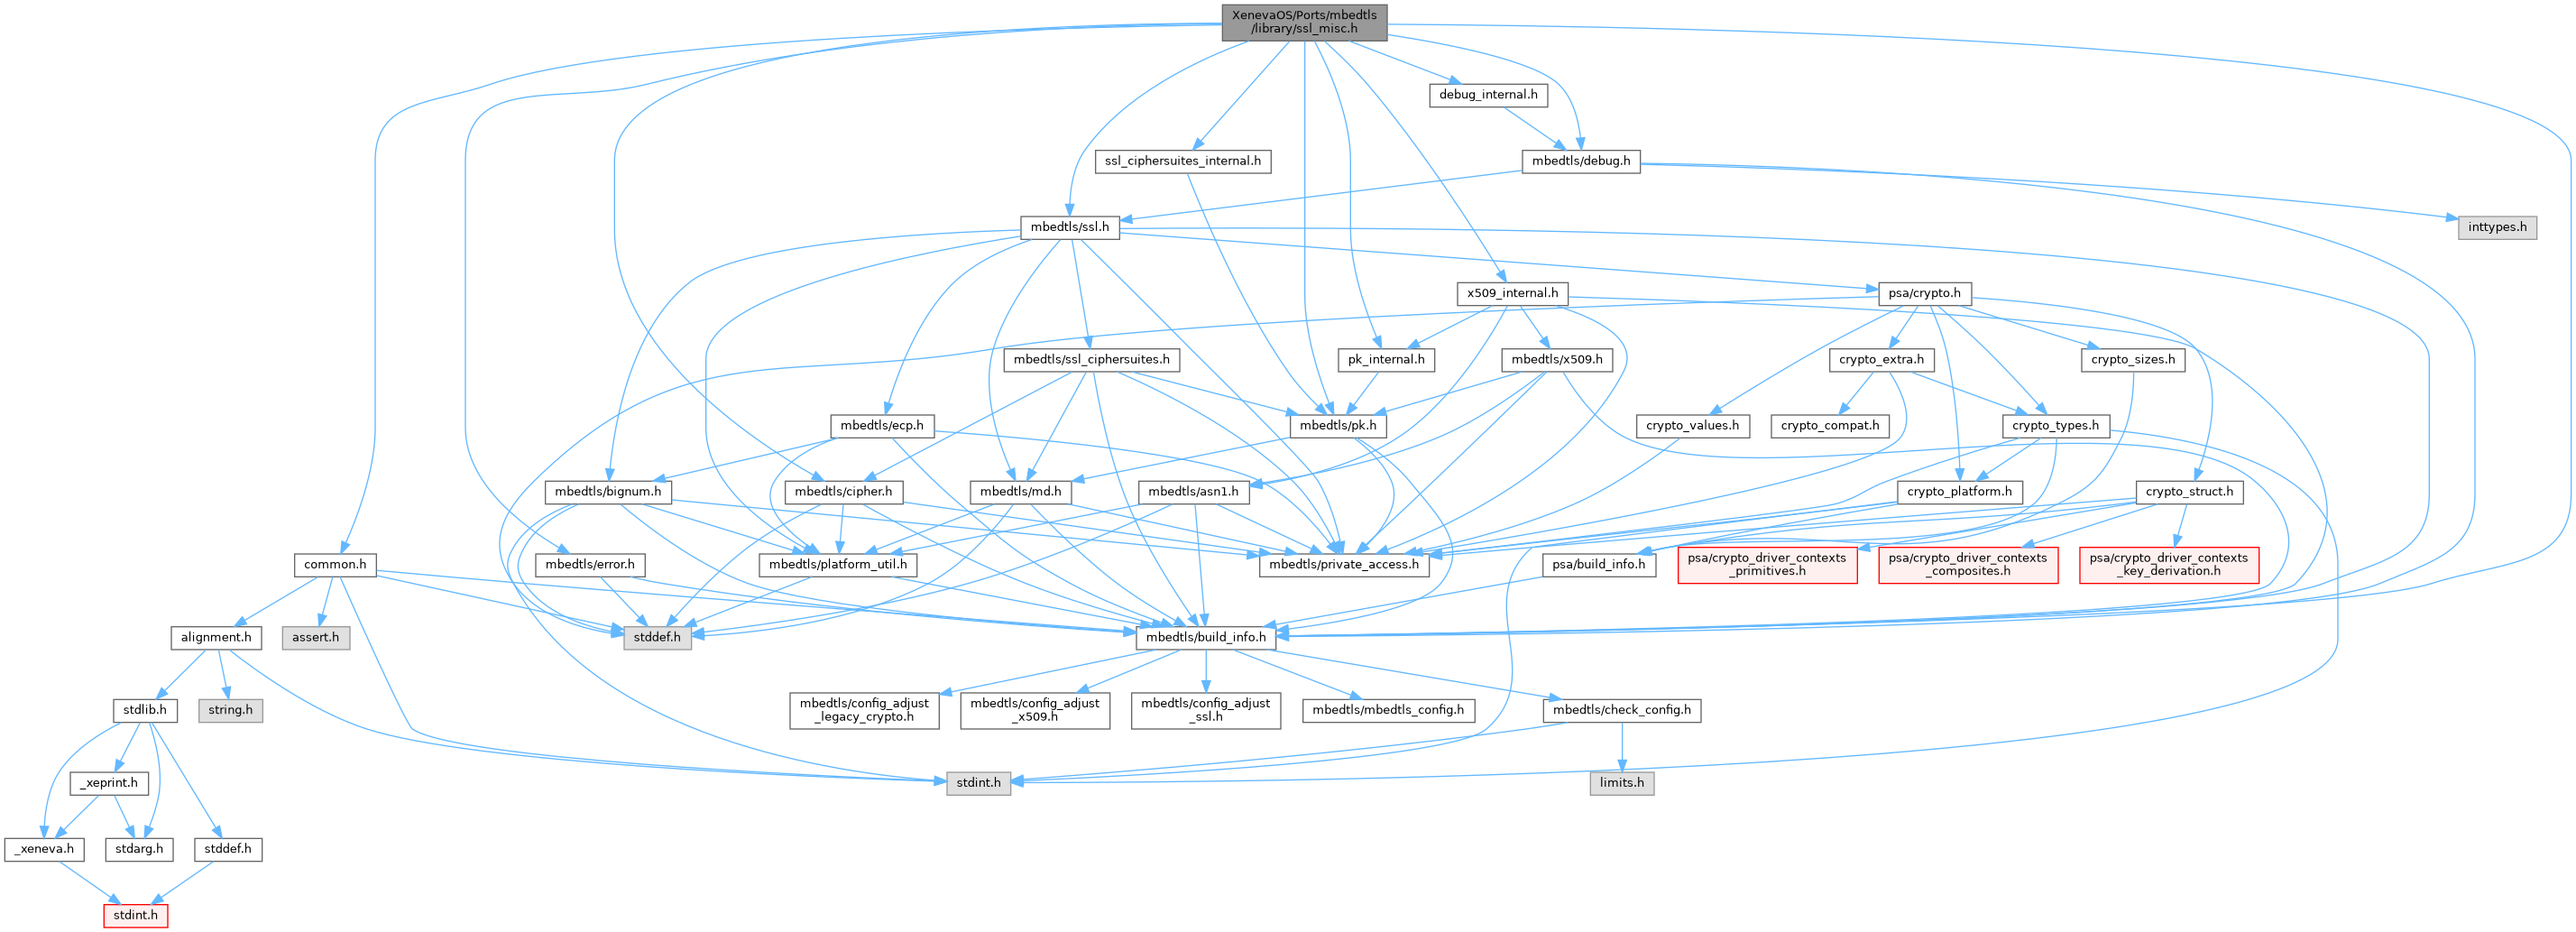
Go to the source code of this file.
Classes | |
| struct | mbedtls_ssl_key_set |
| The data structure holding the cryptographic material (key and IV) used for record protection in TLS 1.3. More... | |
| struct | mbedtls_ssl_tls13_early_secrets |
| struct | mbedtls_ssl_tls13_handshake_secrets |
| struct | mbedtls_ssl_handshake_params |
| struct | mbedtls_ssl_transform |
| struct | mbedtls_record |
Typedefs | |
| typedef int | mbedtls_ssl_tls_prf_cb(const unsigned char *secret, size_t slen, const char *label, const unsigned char *random, size_t rlen, unsigned char *dstbuf, size_t dlen) |
| typedef struct mbedtls_ssl_key_set | mbedtls_ssl_key_set |
| typedef struct mbedtls_ssl_hs_buffer | mbedtls_ssl_hs_buffer |
Enumerations | |
| enum | mbedtls_ssl_mode_t { MBEDTLS_SSL_MODE_STREAM = 0 , MBEDTLS_SSL_MODE_CBC , MBEDTLS_SSL_MODE_CBC_ETM , MBEDTLS_SSL_MODE_AEAD } |
| TLS record protection modes. More... | |
Detailed Description
Internal functions shared by the SSL modules.
Macro Definition Documentation
◆ MBEDTLS_CLIENT_HELLO_RANDOM_LEN
| #define MBEDTLS_CLIENT_HELLO_RANDOM_LEN 32 |
◆ MBEDTLS_RECEIVED_SIG_ALGS_SIZE
| #define MBEDTLS_RECEIVED_SIG_ALGS_SIZE 20 |
◆ MBEDTLS_SERVER_HELLO_RANDOM_LEN
| #define MBEDTLS_SERVER_HELLO_RANDOM_LEN 32 |
◆ MBEDTLS_SSL_CHK_BUF_PTR
| #define MBEDTLS_SSL_CHK_BUF_PTR | ( | cur, | |
| end, | |||
| need | |||
| ) |
This macro checks if the remaining size in a buffer is greater or equal than a needed space. If it is not the case, it returns an SSL_BUFFER_TOO_SMALL error.
- Parameters
-
cur Pointer to the current position in the buffer. end Pointer to one past the end of the buffer. need Needed space in bytes.
◆ MBEDTLS_SSL_CHK_BUF_READ_PTR
| #define MBEDTLS_SSL_CHK_BUF_READ_PTR | ( | cur, | |
| end, | |||
| need | |||
| ) |
This macro checks if the remaining length in an input buffer is greater or equal than a needed length. If it is not the case, it returns MBEDTLS_ERR_SSL_DECODE_ERROR error and pends a MBEDTLS_SSL_ALERT_MSG_DECODE_ERROR alert message.
This is a function-like macro. It is guaranteed to evaluate each argument exactly once.
- Parameters
-
cur Pointer to the current position in the buffer. end Pointer to one past the end of the buffer. need Needed length in bytes.
◆ MBEDTLS_SSL_CID_LEN_MAX
| #define MBEDTLS_SSL_CID_LEN_MAX MBEDTLS_SSL_CID_IN_LEN_MAX |
◆ MBEDTLS_SSL_EXT_ID_ALPN
| #define MBEDTLS_SSL_EXT_ID_ALPN 8 |
◆ MBEDTLS_SSL_EXT_ID_CERT_AUTH
| #define MBEDTLS_SSL_EXT_ID_CERT_AUTH 18 |
◆ MBEDTLS_SSL_EXT_ID_CLI_CERT_TYPE
| #define MBEDTLS_SSL_EXT_ID_CLI_CERT_TYPE 10 |
◆ MBEDTLS_SSL_EXT_ID_COOKIE
| #define MBEDTLS_SSL_EXT_ID_COOKIE 16 |
◆ MBEDTLS_SSL_EXT_ID_EARLY_DATA
| #define MBEDTLS_SSL_EXT_ID_EARLY_DATA 14 |
◆ MBEDTLS_SSL_EXT_ID_ENCRYPT_THEN_MAC
| #define MBEDTLS_SSL_EXT_ID_ENCRYPT_THEN_MAC 25 |
◆ MBEDTLS_SSL_EXT_ID_EXTENDED_MASTER_SECRET
| #define MBEDTLS_SSL_EXT_ID_EXTENDED_MASTER_SECRET 26 |
◆ MBEDTLS_SSL_EXT_ID_HEARTBEAT
| #define MBEDTLS_SSL_EXT_ID_HEARTBEAT 7 |
◆ MBEDTLS_SSL_EXT_ID_KEY_SHARE
| #define MBEDTLS_SSL_EXT_ID_KEY_SHARE 22 |
◆ MBEDTLS_SSL_EXT_ID_MAX_FRAGMENT_LENGTH
| #define MBEDTLS_SSL_EXT_ID_MAX_FRAGMENT_LENGTH 2 |
◆ MBEDTLS_SSL_EXT_ID_OID_FILTERS
| #define MBEDTLS_SSL_EXT_ID_OID_FILTERS 19 |
◆ MBEDTLS_SSL_EXT_ID_PADDING
| #define MBEDTLS_SSL_EXT_ID_PADDING 12 |
◆ MBEDTLS_SSL_EXT_ID_POST_HANDSHAKE_AUTH
| #define MBEDTLS_SSL_EXT_ID_POST_HANDSHAKE_AUTH 20 |
◆ MBEDTLS_SSL_EXT_ID_PRE_SHARED_KEY
| #define MBEDTLS_SSL_EXT_ID_PRE_SHARED_KEY 13 |
◆ MBEDTLS_SSL_EXT_ID_PSK_KEY_EXCHANGE_MODES
| #define MBEDTLS_SSL_EXT_ID_PSK_KEY_EXCHANGE_MODES 17 |
◆ MBEDTLS_SSL_EXT_ID_RECORD_SIZE_LIMIT
| #define MBEDTLS_SSL_EXT_ID_RECORD_SIZE_LIMIT 28 |
◆ MBEDTLS_SSL_EXT_ID_SCT
| #define MBEDTLS_SSL_EXT_ID_SCT 9 |
◆ MBEDTLS_SSL_EXT_ID_SERV_CERT_TYPE
| #define MBEDTLS_SSL_EXT_ID_SERV_CERT_TYPE 11 |
◆ MBEDTLS_SSL_EXT_ID_SERVERNAME
| #define MBEDTLS_SSL_EXT_ID_SERVERNAME 1 |
◆ MBEDTLS_SSL_EXT_ID_SERVERNAME_HOSTNAME
| #define MBEDTLS_SSL_EXT_ID_SERVERNAME_HOSTNAME 1 |
◆ MBEDTLS_SSL_EXT_ID_SESSION_TICKET
| #define MBEDTLS_SSL_EXT_ID_SESSION_TICKET 27 |
◆ MBEDTLS_SSL_EXT_ID_SIG_ALG
| #define MBEDTLS_SSL_EXT_ID_SIG_ALG 5 |
◆ MBEDTLS_SSL_EXT_ID_SIG_ALG_CERT
| #define MBEDTLS_SSL_EXT_ID_SIG_ALG_CERT 21 |
◆ MBEDTLS_SSL_EXT_ID_STATUS_REQUEST
| #define MBEDTLS_SSL_EXT_ID_STATUS_REQUEST 3 |
◆ MBEDTLS_SSL_EXT_ID_SUPPORTED_ELLIPTIC_CURVES
| #define MBEDTLS_SSL_EXT_ID_SUPPORTED_ELLIPTIC_CURVES 4 |
◆ MBEDTLS_SSL_EXT_ID_SUPPORTED_GROUPS
| #define MBEDTLS_SSL_EXT_ID_SUPPORTED_GROUPS 4 |
◆ MBEDTLS_SSL_EXT_ID_SUPPORTED_POINT_FORMATS
| #define MBEDTLS_SSL_EXT_ID_SUPPORTED_POINT_FORMATS 24 |
◆ MBEDTLS_SSL_EXT_ID_SUPPORTED_VERSIONS
| #define MBEDTLS_SSL_EXT_ID_SUPPORTED_VERSIONS 15 |
◆ MBEDTLS_SSL_EXT_ID_TRUNCATED_HMAC
| #define MBEDTLS_SSL_EXT_ID_TRUNCATED_HMAC 23 |
◆ MBEDTLS_SSL_EXT_ID_UNRECOGNIZED
| #define MBEDTLS_SSL_EXT_ID_UNRECOGNIZED 0 |
◆ MBEDTLS_SSL_EXT_ID_USE_SRTP
| #define MBEDTLS_SSL_EXT_ID_USE_SRTP 6 |
◆ MBEDTLS_SSL_EXT_MASK
| #define MBEDTLS_SSL_EXT_MASK | ( | id | ) | (1ULL << (MBEDTLS_SSL_EXT_ID_##id)) |
◆ MBEDTLS_SSL_EXT_MASK_NONE
| #define MBEDTLS_SSL_EXT_MASK_NONE 0 |
◆ MBEDTLS_SSL_HEADER_LEN
| #define MBEDTLS_SSL_HEADER_LEN 13 |
◆ MBEDTLS_SSL_IN_BUFFER_LEN
| #define MBEDTLS_SSL_IN_BUFFER_LEN ((MBEDTLS_SSL_HEADER_LEN) + (MBEDTLS_SSL_IN_PAYLOAD_LEN)) |
◆ MBEDTLS_SSL_IN_PAYLOAD_LEN
| #define MBEDTLS_SSL_IN_PAYLOAD_LEN |
◆ MBEDTLS_SSL_INITIAL_HANDSHAKE
| #define MBEDTLS_SSL_INITIAL_HANDSHAKE 0 |
◆ MBEDTLS_SSL_MAC_ADD
| #define MBEDTLS_SSL_MAC_ADD 16 |
◆ MBEDTLS_SSL_MAX_BLOCK_LENGTH
| #define MBEDTLS_SSL_MAX_BLOCK_LENGTH 16 |
◆ MBEDTLS_SSL_MAX_BUFFERED_HS
| #define MBEDTLS_SSL_MAX_BUFFERED_HS 4 |
◆ MBEDTLS_SSL_MAX_CID_EXPANSION
| #define MBEDTLS_SSL_MAX_CID_EXPANSION 0 |
◆ MBEDTLS_SSL_MAX_CURVE_LIST_LEN
| #define MBEDTLS_SSL_MAX_CURVE_LIST_LEN 65535 |
◆ MBEDTLS_SSL_MAX_IV_LENGTH
| #define MBEDTLS_SSL_MAX_IV_LENGTH 16 |
◆ MBEDTLS_SSL_MAX_KEY_LENGTH
| #define MBEDTLS_SSL_MAX_KEY_LENGTH 32 |
◆ MBEDTLS_SSL_MAX_SIG_ALG_LIST_LEN
| #define MBEDTLS_SSL_MAX_SIG_ALG_LIST_LEN 65534 |
◆ MBEDTLS_SSL_MIN_SIG_ALG_LIST_LEN
| #define MBEDTLS_SSL_MIN_SIG_ALG_LIST_LEN 2 |
◆ MBEDTLS_SSL_OUT_BUFFER_LEN
| #define MBEDTLS_SSL_OUT_BUFFER_LEN ((MBEDTLS_SSL_HEADER_LEN) + (MBEDTLS_SSL_OUT_PAYLOAD_LEN)) |
◆ MBEDTLS_SSL_OUT_PAYLOAD_LEN
| #define MBEDTLS_SSL_OUT_PAYLOAD_LEN |
◆ MBEDTLS_SSL_PADDING_ADD
| #define MBEDTLS_SSL_PADDING_ADD 0 |
◆ MBEDTLS_SSL_PAYLOAD_OVERHEAD
| #define MBEDTLS_SSL_PAYLOAD_OVERHEAD |
◆ MBEDTLS_SSL_PEND_FATAL_ALERT
| #define MBEDTLS_SSL_PEND_FATAL_ALERT | ( | type, | |
| user_return_value | |||
| ) | mbedtls_ssl_pend_fatal_alert(ssl, type, user_return_value) |
◆ MBEDTLS_SSL_PROC_CHK
| #define MBEDTLS_SSL_PROC_CHK | ( | f | ) |
◆ MBEDTLS_SSL_PROC_CHK_NEG
| #define MBEDTLS_SSL_PROC_CHK_NEG | ( | f | ) |
◆ MBEDTLS_SSL_RENEGOTIATION_DONE
| #define MBEDTLS_SSL_RENEGOTIATION_DONE 2 /* Done or aborted */ |
◆ MBEDTLS_SSL_RENEGOTIATION_IN_PROGRESS
| #define MBEDTLS_SSL_RENEGOTIATION_IN_PROGRESS 1 /* In progress */ |
◆ MBEDTLS_SSL_RENEGOTIATION_PENDING
| #define MBEDTLS_SSL_RENEGOTIATION_PENDING 3 /* Requested (server only) */ |
◆ MBEDTLS_SSL_RETRANS_FINISHED
| #define MBEDTLS_SSL_RETRANS_FINISHED 3 |
◆ MBEDTLS_SSL_RETRANS_PREPARING
| #define MBEDTLS_SSL_RETRANS_PREPARING 0 |
◆ MBEDTLS_SSL_RETRANS_SENDING
| #define MBEDTLS_SSL_RETRANS_SENDING 1 |
◆ MBEDTLS_SSL_RETRANS_WAITING
| #define MBEDTLS_SSL_RETRANS_WAITING 2 |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CH
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CH |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CR
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CR |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CT
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_CT |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_EE
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_EE |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_HRR
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_HRR |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_NST
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_NST |
◆ MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_SH
| #define MBEDTLS_SSL_TLS1_3_ALLOWED_EXTS_OF_SH |
◆ MBEDTLS_SSL_TLS1_3_EXT_MASK_UNRECOGNIZED
| #define MBEDTLS_SSL_TLS1_3_EXT_MASK_UNRECOGNIZED |
◆ MBEDTLS_SSL_TLS1_3_HS_HELLO_RETRY_REQUEST
| #define MBEDTLS_SSL_TLS1_3_HS_HELLO_RETRY_REQUEST (-MBEDTLS_SSL_HS_SERVER_HELLO) |
◆ MBEDTLS_TLS_EXT_ADV_CONTENT_LEN
| #define MBEDTLS_TLS_EXT_ADV_CONTENT_LEN |
◆ MBEDTLS_TLS_EXT_ECJPAKE_KKPP_OK
| #define MBEDTLS_TLS_EXT_ECJPAKE_KKPP_OK (1 << 1) |
◆ MBEDTLS_TLS_EXT_SUPPORTED_POINT_FORMATS_PRESENT
| #define MBEDTLS_TLS_EXT_SUPPORTED_POINT_FORMATS_PRESENT (1 << 0) |
Typedef Documentation
◆ mbedtls_ssl_hs_buffer
| typedef struct mbedtls_ssl_hs_buffer mbedtls_ssl_hs_buffer |
◆ mbedtls_ssl_key_set
| typedef struct mbedtls_ssl_key_set mbedtls_ssl_key_set |
◆ mbedtls_ssl_tls_prf_cb
| typedef int mbedtls_ssl_tls_prf_cb(const unsigned char *secret, size_t slen, const char *label, const unsigned char *random, size_t rlen, unsigned char *dstbuf, size_t dlen) |
Enumeration Type Documentation
◆ mbedtls_ssl_mode_t
| enum mbedtls_ssl_mode_t |
Function Documentation
◆ mbedtls_ssl_add_hs_hdr_to_checksum()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_add_hs_hdr_to_checksum | ( | mbedtls_ssl_context * | ssl, |
| unsigned | hs_type, | ||
| size_t | total_hs_len | ||
| ) |
◆ mbedtls_ssl_add_hs_msg_to_checksum()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_add_hs_msg_to_checksum | ( | mbedtls_ssl_context * | ssl, |
| unsigned | hs_type, | ||
| unsigned char const * | msg, | ||
| size_t | msg_len | ||
| ) |
◆ mbedtls_ssl_check_curve_tls_id()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_check_curve_tls_id | ( | const mbedtls_ssl_context * | ssl, |
| uint16_t | tls_id | ||
| ) |
◆ mbedtls_ssl_check_timer()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_check_timer | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_decrypt_buf()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_decrypt_buf | ( | mbedtls_ssl_context const * | ssl, |
| mbedtls_ssl_transform * | transform, | ||
| mbedtls_record * | rec | ||
| ) |
◆ mbedtls_ssl_encrypt_buf()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_encrypt_buf | ( | mbedtls_ssl_context * | ssl, |
| mbedtls_ssl_transform * | transform, | ||
| mbedtls_record * | rec, | ||
| int(*)(void *, unsigned char *, size_t) | f_rng, | ||
| void * | p_rng | ||
| ) |
◆ mbedtls_ssl_fetch_input()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_fetch_input | ( | mbedtls_ssl_context * | ssl, |
| size_t | nb_want | ||
| ) |
◆ mbedtls_ssl_finish_handshake_msg()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_finish_handshake_msg | ( | mbedtls_ssl_context * | ssl, |
| size_t | buf_len, | ||
| size_t | msg_len | ||
| ) |
◆ mbedtls_ssl_flush_output()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_flush_output | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_get_ecp_group_id_from_tls_id()
| mbedtls_ecp_group_id mbedtls_ssl_get_ecp_group_id_from_tls_id | ( | uint16_t | tls_id | ) |
Return mbedtls_ecp_group_id for the specified TLS ID.
- Parameters
-
tls_id The TLS ID to look for
- Returns
- Proper
mbedtls_ecp_group_idif the TLS ID is supported, or MBEDTLS_ECP_DP_NONE otherwise
◆ mbedtls_ssl_get_extension_id()
| uint32_t mbedtls_ssl_get_extension_id | ( | unsigned int | extension_type | ) |
◆ mbedtls_ssl_get_extension_mask()
| uint32_t mbedtls_ssl_get_extension_mask | ( | unsigned int | extension_type | ) |
◆ mbedtls_ssl_get_handshake_transcript()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_get_handshake_transcript | ( | mbedtls_ssl_context * | ssl, |
| const mbedtls_md_type_t | md, | ||
| unsigned char * | dst, | ||
| size_t | dst_len, | ||
| size_t * | olen | ||
| ) |
◆ mbedtls_ssl_get_mode_from_ciphersuite()
| mbedtls_ssl_mode_t mbedtls_ssl_get_mode_from_ciphersuite | ( | const mbedtls_ssl_ciphersuite_t * | suite | ) |
◆ mbedtls_ssl_get_mode_from_transform()
| mbedtls_ssl_mode_t mbedtls_ssl_get_mode_from_transform | ( | const mbedtls_ssl_transform * | transform | ) |
◆ mbedtls_ssl_get_psa_curve_info_from_tls_id()
| int mbedtls_ssl_get_psa_curve_info_from_tls_id | ( | uint16_t | tls_id, |
| psa_key_type_t * | type, | ||
| size_t * | bits | ||
| ) |
Return PSA EC info for the specified TLS ID.
- Parameters
-
tls_id The TLS ID to look for type If the TLD ID is supported, then proper psa_key_type_tvalue is returned here. Can be NULL.bits If the TLD ID is supported, then proper bit size is returned here. Can be NULL.
- Returns
- PSA_SUCCESS if the TLS ID is supported, PSA_ERROR_NOT_SUPPORTED otherwise
- Note
- If either
familyorbitsparameters are NULL, then the corresponding value is not returned. The function can be called with both parameters as NULL simply to check if a specific TLS ID is supported.
◆ mbedtls_ssl_get_tls_id_from_ecp_group_id()
| uint16_t mbedtls_ssl_get_tls_id_from_ecp_group_id | ( | mbedtls_ecp_group_id | grp_id | ) |
Return TLS ID for the specified mbedtls_ecp_group_id.
- Parameters
-
grp_id The mbedtls_ecp_group_idID to look for
- Returns
- Proper TLS ID if the
mbedtls_ecp_group_idis supported, or 0 otherwise
◆ mbedtls_ssl_handle_message_type()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_handle_message_type | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_handle_pending_alert()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_handle_pending_alert | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_handshake_client_step()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_handshake_client_step | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_handshake_free()
| void mbedtls_ssl_handshake_free | ( | mbedtls_ssl_context * | ssl | ) |
Free referenced items in an SSL handshake context and clear memory.
- Parameters
-
ssl SSL context
◆ mbedtls_ssl_handshake_server_step()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_handshake_server_step | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_handshake_wrapup()
| void mbedtls_ssl_handshake_wrapup | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_handshake_wrapup_free_hs_transform()
| void mbedtls_ssl_handshake_wrapup_free_hs_transform | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_hash_from_md_alg()
| unsigned char mbedtls_ssl_hash_from_md_alg | ( | int | md | ) |
◆ mbedtls_ssl_md_alg_from_hash()
| mbedtls_md_type_t mbedtls_ssl_md_alg_from_hash | ( | unsigned char | hash | ) |
◆ mbedtls_ssl_optimize_checksum()
| void mbedtls_ssl_optimize_checksum | ( | mbedtls_ssl_context * | ssl, |
| const mbedtls_ssl_ciphersuite_t * | ciphersuite_info | ||
| ) |
◆ mbedtls_ssl_parse_certificate()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_parse_certificate | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_parse_change_cipher_spec()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_parse_change_cipher_spec | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_parse_finished()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_parse_finished | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_pend_fatal_alert()
| void mbedtls_ssl_pend_fatal_alert | ( | mbedtls_ssl_context * | ssl, |
| unsigned char | alert_type, | ||
| int | alert_reason | ||
| ) |
◆ mbedtls_ssl_prepare_handshake_record()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_prepare_handshake_record | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_read_record()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_read_record | ( | mbedtls_ssl_context * | ssl, |
| unsigned | update_hs_digest | ||
| ) |
Update record layer.
         This function roughly separates the implementation
         of the logic of (D)TLS from the implementation
         of the secure transport.
- Parameters
-
ssl The SSL context to use. update_hs_digest This indicates if the handshake digest should be automatically updated in case a handshake message is found.
- Returns
- 0 or non-zero error code.
- Note
- A clarification on what is called 'record layer' here is in order, as many sensible definitions are possible:
The record layer takes as input an untrusted underlying transport (stream or datagram) and transforms it into a serially multiplexed, secure transport, which conceptually provides the following:
(1) Three datagram based, content-agnostic transports for handshake, alert and CCS messages. (2) One stream- or datagram-based transport for application data. (3) Functionality for changing the underlying transform securing the contents.
The interface to this functionality is given as follows:
a Updating [Currently implemented by mbedtls_ssl_read_record]
Check if and on which of the four 'ports' data is pending: Nothing, a controlling datagram of type (1), or application data (2). In any case data is present, internal buffers provide access to the data for the user to process it. Consumption of type (1) datagrams is done automatically on the next update, invalidating that the internal buffers for previous datagrams, while consumption of application data (2) is user-controlled.
b Reading of application data [Currently manual adaption of ssl->in_offt pointer]
As mentioned in the last paragraph, consumption of data is different from the automatic consumption of control datagrams (1) because application data is treated as a stream.
c Tracking availability of application data [Currently manually through decreasing ssl->in_msglen]
For efficiency and to retain datagram semantics for application data in case of DTLS, the record layer provides functionality for checking how much application data is still available in the internal buffer.
d Changing the transformation securing the communication.
Given an opaque implementation of the record layer in the above sense, it should be possible to implement the logic of (D)TLS on top of it without the need to know anything about the record layer's internals. This is done e.g. in all the handshake handling functions, and in the application data reading function mbedtls_ssl_read.
- Note
- The above tries to give a conceptual picture of the record layer, but the current implementation deviates from it in some places. For example, our implementation of the update functionality through mbedtls_ssl_read_record discards datagrams depending on the current state, which wouldn't fall under the record layer's responsibility following the above definition.
◆ mbedtls_ssl_read_version()
| uint16_t mbedtls_ssl_read_version | ( | const unsigned char | version[2], |
| int | transport | ||
| ) |
◆ mbedtls_ssl_reset_checksum()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_reset_checksum | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_reset_in_pointers()
| void mbedtls_ssl_reset_in_pointers | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_reset_out_pointers()
| void mbedtls_ssl_reset_out_pointers | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_send_fatal_handshake_failure()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_send_fatal_handshake_failure | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_session_copy()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_session_copy | ( | mbedtls_ssl_session * | dst, |
| const mbedtls_ssl_session * | src | ||
| ) |
◆ mbedtls_ssl_session_reset_int()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_session_reset_int | ( | mbedtls_ssl_context * | ssl, |
| int | partial | ||
| ) |
◆ mbedtls_ssl_session_reset_msg_layer()
| void mbedtls_ssl_session_reset_msg_layer | ( | mbedtls_ssl_context * | ssl, |
| int | partial | ||
| ) |
◆ mbedtls_ssl_set_inbound_transform()
| void mbedtls_ssl_set_inbound_transform | ( | mbedtls_ssl_context * | ssl, |
| mbedtls_ssl_transform * | transform | ||
| ) |
◆ mbedtls_ssl_set_outbound_transform()
| void mbedtls_ssl_set_outbound_transform | ( | mbedtls_ssl_context * | ssl, |
| mbedtls_ssl_transform * | transform | ||
| ) |
◆ mbedtls_ssl_set_timer()
| void mbedtls_ssl_set_timer | ( | mbedtls_ssl_context * | ssl, |
| uint32_t | millisecs | ||
| ) |
◆ mbedtls_ssl_start_handshake_msg()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_start_handshake_msg | ( | mbedtls_ssl_context * | ssl, |
| unsigned char | hs_type, | ||
| unsigned char ** | buf, | ||
| size_t * | buf_len | ||
| ) |
◆ mbedtls_ssl_transform_free()
| void mbedtls_ssl_transform_free | ( | mbedtls_ssl_transform * | transform | ) |
Free referenced items in an SSL transform context and clear memory.
- Parameters
-
transform SSL transform context
◆ mbedtls_ssl_transform_init()
| void mbedtls_ssl_transform_init | ( | mbedtls_ssl_transform * | transform | ) |
◆ mbedtls_ssl_update_handshake_status()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_update_handshake_status | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_update_in_pointers()
| void mbedtls_ssl_update_in_pointers | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_update_out_pointers()
| void mbedtls_ssl_update_out_pointers | ( | mbedtls_ssl_context * | ssl, |
| mbedtls_ssl_transform * | transform | ||
| ) |
◆ mbedtls_ssl_validate_ciphersuite()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_validate_ciphersuite | ( | const mbedtls_ssl_context * | ssl, |
| const mbedtls_ssl_ciphersuite_t * | suite_info, | ||
| mbedtls_ssl_protocol_version | min_tls_version, | ||
| mbedtls_ssl_protocol_version | max_tls_version | ||
| ) |
Validate cipher suite against config in SSL context.
- Parameters
-
ssl SSL context suite_info Cipher suite to validate min_tls_version Minimal TLS version to accept a cipher suite max_tls_version Maximal TLS version to accept a cipher suite
- Returns
- 0 if valid, negative value otherwise.
◆ mbedtls_ssl_write_certificate()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_write_certificate | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_write_change_cipher_spec()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_write_change_cipher_spec | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_write_finished()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_write_finished | ( | mbedtls_ssl_context * | ssl | ) |
◆ mbedtls_ssl_write_handshake_msg_ext()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_write_handshake_msg_ext | ( | mbedtls_ssl_context * | ssl, |
| int | update_checksum, | ||
| int | force_flush | ||
| ) |
◆ mbedtls_ssl_write_record()
| MBEDTLS_CHECK_RETURN_CRITICAL int mbedtls_ssl_write_record | ( | mbedtls_ssl_context * | ssl, |
| int | force_flush | ||
| ) |
◆ mbedtls_ssl_write_version()
| void mbedtls_ssl_write_version | ( | unsigned char | version[2], |
| int | transport, | ||
| mbedtls_ssl_protocol_version | tls_version | ||
| ) |
